
All Resources
Webinar
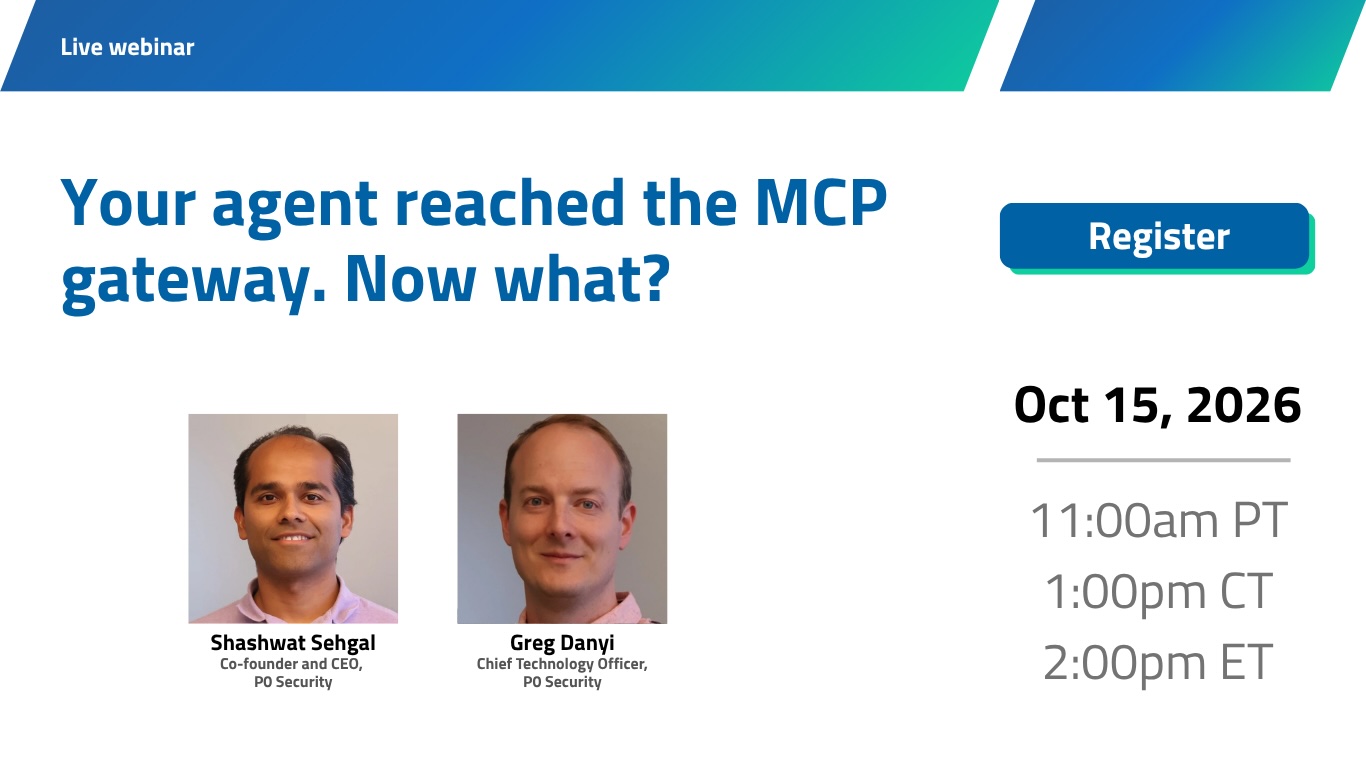
Your agent reached the MCP gateway. Now what?
See where MCP gateways fit in the agentic action chain, what they control and how authorization is handled for access to sensitive systems.
No results found.
Case study
Fortune 50 CPG company deploys runtime agent access control
P0 Security set up a runtime authorization layer across three AI agent architectures in the organization's GCP environment, using its identity provider for inbound authentication and native GCP mechanisms for
Webinar
Your agent reached the MCP gateway. Now what?
See where MCP gateways fit in the agentic action chain, what they control and how authorization is handled for access to sensitive systems.
Webinar
Agentic runtime access control
Agent security vendors cover different parts of the problem. See how Network/API, MCP, DSPM, and identity-led approaches map across the agentic action chain.
Video
Controlling agent access beyond MCP gateways
See how P0 evaluates policy across the full agentic action chain to allow, deny, or route requests for human approval—beyond what an MCP gateway can see.
Datasheet
Runtime access control for every identity
See how P0 governs what AI agents, humans and workloads can do with one policy layer and just-in-time access to sensitive systems.
Datasheet
Runtime access control for AI agents
Learn how P0 preserves originator and agent identity, authorizes tool calls at runtime and limits access to exactly what each task requires.
Report
Anatomy of an agentic outage
See how standing privilege, an unmanaged credential and missing runtime controls turn an agent action into a production outage in nine seconds.
Case study
AI security company brings access under central policy framework
See how an AI security company used P0 to replace standing GCP and SSH privileges with centralized, just-in-time developer access.
Whitepaper
A practical path from standing privilege to runtime access control
Understand what is driving the need to move beyond traditional, vault-centric PAM. These frameworks examine common migration and adoption triggers.
Webinar
Five use cases for runtime authorization
How to calibrate integration depth to resource sensitivity, identify where fine-grained control is most critical and move toward Zero Standing Privilege across users, service accounts and AI agents.
Video
Just-in-time RDP access
See how P0 enables just-in-time RDP access through the CLI, authenticating users via their IdP and eliminating shared accounts while creating a complete, audit-ready session record.
Video
P0 Runtime Access platform for Zscaler private access
See how Zscaler provides secure connectivity to private resources as P0 governs what users can do once connected, enabling fine-grained, just-in-time access without standing privilege risk.
Video
Runtime agent controller
In this fly-through, you'll see how agents start with zero standing privilege and operate under runtime guardrails enforced by the P0 Agent Controller, enabling secure just-in-time access.
Video
The real risk with AI agents isn’t rogue behavior
The biggest AI agent risk may not be a rogue agent. It may be an over-permissioned one. See how P0 controls access across the full action chain.
Video
Runtime access control for AI agents
AI agents can complete the task and still access too much. Watch how P0 enforces runtime access control across the full agent action chain.
Report
The authorization layer is where modern privilege lives
Identity and access management is changing fast. IGA, PAM, NHIs and AI agents are starting to collide, and security teams need a better way to govern access across all of
Webinar
The identity layers behind AI agent access
Before you govern AI agents, make sure you're governing what they're inheriting. See how identity hygiene becomes the foundation of agent authorization.
Webinar
Not your grandma's identity governance
AWS and HubSpot are not the same governance problem — but most teams treat them like they are. See how integration depth should track resource sensitivity, and why AI agents
Video
Secure cloud access without standing privilege
Watch SSH access through ZPA become identity-based, time-bound and approval-driven instead of relying on standing access and shared accounts.
Webinar
The last mile of Zero Trust for Zscaler customers
Secure access is only part of Zero Trust. This session covers how to reduce standing privilege, govern cloud entitlements and handle non-human identities once connectivity is already in place.
Webinar
An introduction to agentic identity security
AI agents are showing up fast, but most teams lack a clear way to secure them. Learn what they are, where IAM falls short and how to control what they
Report
How PAM is evolving for cloud, NHIs and AI agents
A new SACR report shows the shift from vault-led PAM to identity-native, just-in-time access. The maturity model will feel familiar. It builds on ideas Shashwat Sehgal has pushed for years.
Report
SANS 2026: Why identity attacks still get through
Based on a large independent SANS survey, this report shows why identity attacks keep succeeding after login and where teams are falling behind on containment, NHIs and AI agents.
Video
Right-size agent and service account access
Why agents and service accounts need ownership and runtime authorization, and how P0 replaces blanket permissions with just-enough privilege, accountability and control at scale in production.
Video
Secure SSH access without shared credentials
See how P0 delivers fast, identity-based SSH access to cloud instances, removes shared accounts and standing credentials, and preserves clean audit trails and session visibility end-to-end.
Video
Secure cloud access without standing privilege
See how P0 grants fast, granular access to AWS resources, replaces broad permissions with just-in-time access, removes shared credentials and keeps every action tied to identity.
Datasheet
Just-in-Time access controls for cloud
P0 Security redefines privileged access for cloud databases by removing shared DB users and credential-based access.
Video
Bring AI agent access under control
Greg and Neha discuss why AI agents need identity-bound, time-scoped access to production environments and what security teams can do to keep innovation under control.
Webinar
Least privilege as business protection: SOC 2 example
Audits expose a hard truth: teams can’t prove who had access, when or why. Learn how to replace standing privilege with JIT access and audit-ready evidence.
Case study
CNA takes control of service account sprawl
Service accounts explode across GCP and suddenly no one knows who owns what. See how CNA cleaned it up with full visibility, no static keys and real governance at scale.
Case study
Applied Intuition streamlines workflows
Access requests, engineers wait times and privileged access took longer than it should. See how Applied Intuition fixed it with just-in-time access, faster approvals and cleaner audits.
Case study
Afresh automates privileged access
Access to sensitive data slowed teams, turned into sprawl and drift. See how Afresh gave engineers fast, just-in-time access across systems while keeping tight control and staying audit.
Case study
Splunk accelerates secure cloud access
Access across AWS, GCP and Azure gets messy fast, and legacy PAM adds friction and risk. See how Splunk gives developers fast, just-in-time access without keys, proxies or overhead.
Case study
CommonLit enforces SOC 2 controls
Security pressure is rising but small teams can’t afford slow access or heavy tools. See how CommonLit keeps engineers moving with just-in-time access and audit-ready control.
Case study
Divvy Homes scales secure production access
Access to sensitive data slows teams down or gets over-granted to keep things moving. See how Divvy replaced legacy PAM with faster, just-in-time access and cleaner control.
Webinar
NHI - Access control for autonomous systems
Autonomous agents assume trust and gain access fast. Learn how to govern them with the right policies so they stay productive, contained and out of sensitive systems.
Webinar
Eliminate static SSH keys and standing access
Static SSH keys and shared access seem fine until they turn into risk and audit headaches. See how to move to short-lived, identity-based access that’s easier to manage.
Solution brief
A buyer’s guide to securing the production stack
Vault-centric PAM breaks in modern environments and adds risk and drag. This guide shows what to require instead, with identity-native controls and just-in-time access across all identities.
Solution brief
A practical guide to governing NHIs
NHIs power cloud, CI/CD and Kubernetes but create a fast-growing attack surface. Learn how to control them with just-enough, just-in-time access, monitoring and lifecycle governance.
Video
Eliminate standing privilege across your cloud
How P0 identifies unused permissions in GCP, use Access Graph and Policy Studio, to fix misconfigurations, automate approvals, and tie all actions to a user’s identity.
Video
How to Sync AWS Access with ServiceNow
Watch how P0 syncs ServiceNow tickets with real-time access provisioning for seamless and auditable AWS access.
Video
A modern solution to the production access lifecycle
Access workflows have changed, but security still runs on old models that can’t keep up. This API-led approach removes static keys and delivers just-in-time access without slowing teams down.
Webinar
Moving from just-in-case to just-in-time
Non-human identities run with persistent permissions and expand your attack surface. Learn how to replace just-in-case access with just-enough, just-in-time controls and real monitoring.
Video
Humans to AI agents: how identity security evolves
IAM, IGA and PAM struggle with today’s complex identity sprawl. This interview shows why they break and how teams can rethink identity security for modern environments.
Video
Secure, fine-grained access to K8s Clusters
Broad access to Kubernetes clusters creates hidden risk. See how to replace it with least-privilege, short-lived access using fine-grained controls.
Solution brief
How to evaluate modern privileged access
Legacy vault workflows create standing access and blind spots. This guide shows how to evaluate modern PAM with just-in-time provisioning, continuous discovery and machine access governance.
Video
Fast, identity-based SSH for developers
Server access is slow, shared and hard to audit. See how developers get fast, identity-tied access with no static keys and approvals in Slack, Teams or ServiceNow.
Webinar
Managing multi-cloud, NHI and AI agent access
New infrastructure and identities are outpacing legacy security models. This session gives a first-principles framework to rethink identity security and plan next steps.
Datasheet
SSH/Sudo access for cloud and on-prem
Static SSH keys and jump hosts slow teams and add risk. See how identity-native, short-lived access secures servers while keeping developer workflows fast and consistent.
Solution brief
Just-in-time production access without the risk
See how Dev/Eng teams are moving faster with real-time access workflows. Learn how leading companies are solving access at scale using P0’s real-time, least privilege access model.
Solution brief
Access hygiene blueprint for AWS
A practical guide that shows how to uncover identity risks in AWS, remove static credentials, right-size roles and build a verified least-privilege foundation ready for JIT access and modernization.
Video
What creates gaps in identity access security
Find out what created gaps in today's identity access security and how the identity stack is evolving.
Whitepaper
The path to Least Privilege deployment guide
If you're struggling with the tradeoff between strong security and developer agility, this is a practical guide to implementing Just-in-Time (JIT) access.
Whitepaper
Cloud access is a mess. Here's a map
A practical field guide to help assess your identity posture across cloud platforms. Built by practitioners, not vendors.
Solution brief
Access control beyond vault limitations
A look at why vault-led PAM struggles in hybrid environments with machines and agents, and why CyberArk and BeyondTrust customers are exploring modern options as they rethink and update their
Solution brief
A guide modernizing or augmenting PAM
You’re trying to stretch legacy PAM like CyberArk to fit modern infrastructure, and it’s breaking. See why keys, vaults and standing access fail and what actually works now.
Datasheet
P0 Security platform at-a-glance
A quick look at P0’s privileged access control plane which automates least-privilege, removes standing access and provides unified governance for users, workloads and agents across hybrid and multi-cloud environments.
Video
Secure OCI access with least privilege and JIT
See how you can go from zero standing access in Oracle Cloud Infrastructure (OCI) to tightly-scoped, time-bound permissions using P0.
Video
Just-in-Time access without slowing devs
Standing access keeps piling up and you know it’s not working. See how CommonLit’s CTO shares a practical way to move to just-in-time access, show value fast and scale without
Solution brief
Secure by design: When agents enter production
Your agents are heading into production with static creds and broad roles, so small mistakes turn into big problems. See the four controls you should put in early to keep
Video
What's driving the need for Zero Standing Privilege
Experts discuss how privileged access has changed with cloud growth and the rise of agentic AI, why authorization matters more than authentication, and how organizations can move toward zero standing
Video
Just-in-time SSH access without keys
A quick demo on how P0 replaces static SSH keys with short-lived, identity-based access using Okta or Entra ID. No vaults, no bastions, no shared accounts.
Video
How to get just-in-time access to RDS Postgres
Learn how P0 grants temporary least privilege access to RDS Postgres with no standing credentials and full identity-level auditability.
Whitepaper
The evolution of privileged access management (PAM)
This paper traces the journey of PAM through three distinct eras: vault-led, bastion-led, and API-led. It highlights why legacy tools break down and what modern environments demand.
Video
Enable JIT SSH access to on-prem machines
Learn how P0 delivers ephemeral SSH access to bare-metal servers via Slack approvals and short-lived certificates.
Video
How to grant time-bound access to AWS RDS
Learn how P0 provides scoped, time-limited PostgreSQL access to AWS RDS via CLI or Slack workflows.
Video
Enforcing AWS access with Microsoft Teams
See how P0 lets you easily grant - and revoke - AWS access directly from within Microsoft Teams.
Whitepaper
CISO guide to approaching identity security programs
Cut through the identity security noise with a first-principles guide that helps CISOs simplify their stack, close real gaps and measure outcomes that matter.
Webinar
Shared secrets to zero standing privilege
In this recording, Principal Security Researcher from Wiz, and CEO of P0 Security walk through the six stages of production access governance maturity.
Video
How to fix standing access in AWS
Learn how P0 identifies and removes unused IAM roles, over-provisioned policies, and dormant credentials.
Video
Elevate machine identity access in GitLab CI/CD
In this 5-minute demo, we show you how P0 enables temporary privilege elevation for GitLab pipelines with scoped access.
Video
Automate credential rotation with GCP and Jira
In this how-to video, discover how P0 automates the entire credential rotation lifecycle and ensures secrets stay fresh.
Video
Enabling JIT admin access for homegrown apps
In this video walkthrough, see how P0 grants temporary admin access to internal apps using a lightweight integration.
Video
Enabling JIT access with Okta (Grafana example)
See how P0 enforces short-lived access for commercial apps by dynamically updating Okta groups and user roles.
Video
The risk of traditional PAM compared to just-in-time
Shashwat Sehgal, CEO and founder of P0, talks about why traditional PAM slows developers down and creates risk, and how P0 flips the model with developer-first, just-in-time access.
Video
P0 leaders on privileged access for all identities
P0 leaders talk about the next generation of privileged access: humans, machines and AI identities.
Video
How to improve mean time to access
In this interview, Cyber Hut founder Simon Moffatt explores how privileged access management must evolve to keep pace with modern hybrid and cloud environments.
Video
A quick fly-through of the P0 Security platform
In this quick demo, we walk through how teams can visualize their entire identity landscape, automate just-in-time access,and simplify governance across cloud and on-prem environments.
Solution brief
Enforcing Least Privilege in AWS/GCP/Azure
Discover how to practically implement and enforce Least Privilege in AWS, GCP, and Azure, reducing risk by eliminating excess permissions, managing identities effectively, and enabling Just-In-Time access control.
No results found.