
Platform | Technology
For users
Deliver least-privileged access for every developer at runtime, replacing standing privilege with identity-driven, policy-based authorization to production systems.
When you don’t know who has access to what or why.
Enterprises are still managing developer access with static credentials, shared accounts and manual approvals that slow teams down and increase risk. Persistent permissions accumulate over time, access reviews fall behind and developers are forced to navigate complex workflows just to get work done.
The result is access that is both over-provisioned and operationally painful.
Solution
Keep teams moving without leaving risky privilege on the table.
P0 replaces static credentials, shared accounts and manual provisioning with dynamic, policy-driven authorization.
Developers request access when they need it. P0 evaluates the request against policy and provisions just-enough privilege, just-in-time.
No vaults. No shared keys. No disruption to developer workflows. Just fast, auditable access tied to a verified identity.
Secure access should be easy to use
When access is fast, predictable and built into familiar workflows, teams are more likely to follow the secure path.
One access model for every type of human access
Whether someone connects directly, needs temporary elevated access or initiates work through an agent, P0 keeps access tied to verified identity, policy and least privilege.
Human-initiated access
Keep the human originator tied to the agent and its actions, so access decisions reflects how the task was started, what the agent is doing and why.
Just-in-time
access
Replace standing privilege with temporary access that is provisioned when needed and removed when the work is done.
SSH and RDP
access
Give engineers direct access to servers using their existing identities without persistent keys, shared credentials or bastion infrastructure.
Emergency
response
Give on-call responders fast access during critical incidents while keeping elevated privilege controlled, time-bound and auditable.
Least-privileged, auditable and agile access people will actually use
P0 centralizes how privileged access is requested, approved and enforced across your production environment. Runtime authorization eliminates standing privilege while keeping every access decision scoped, time-bound and tied to an accountable user identity, whether the user acts directly or initiates work through an agent.
Identity-first authorization
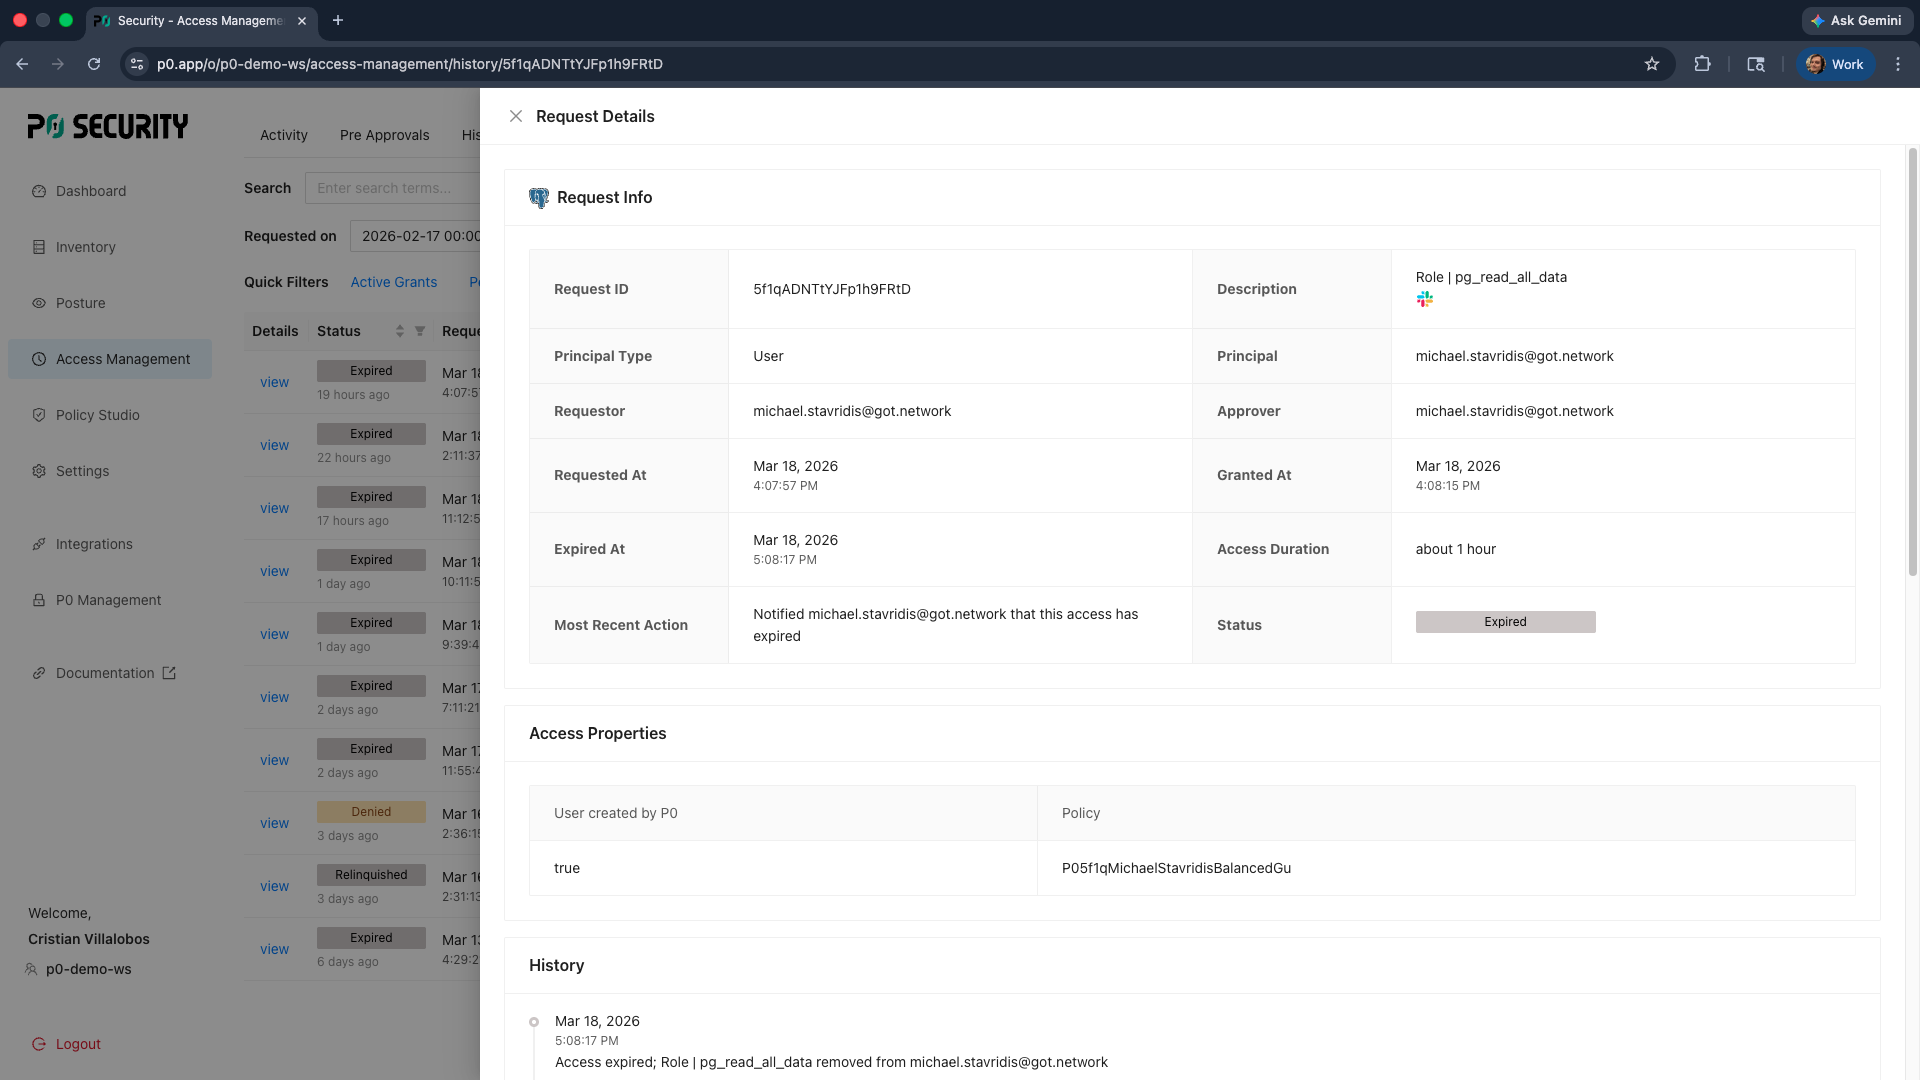
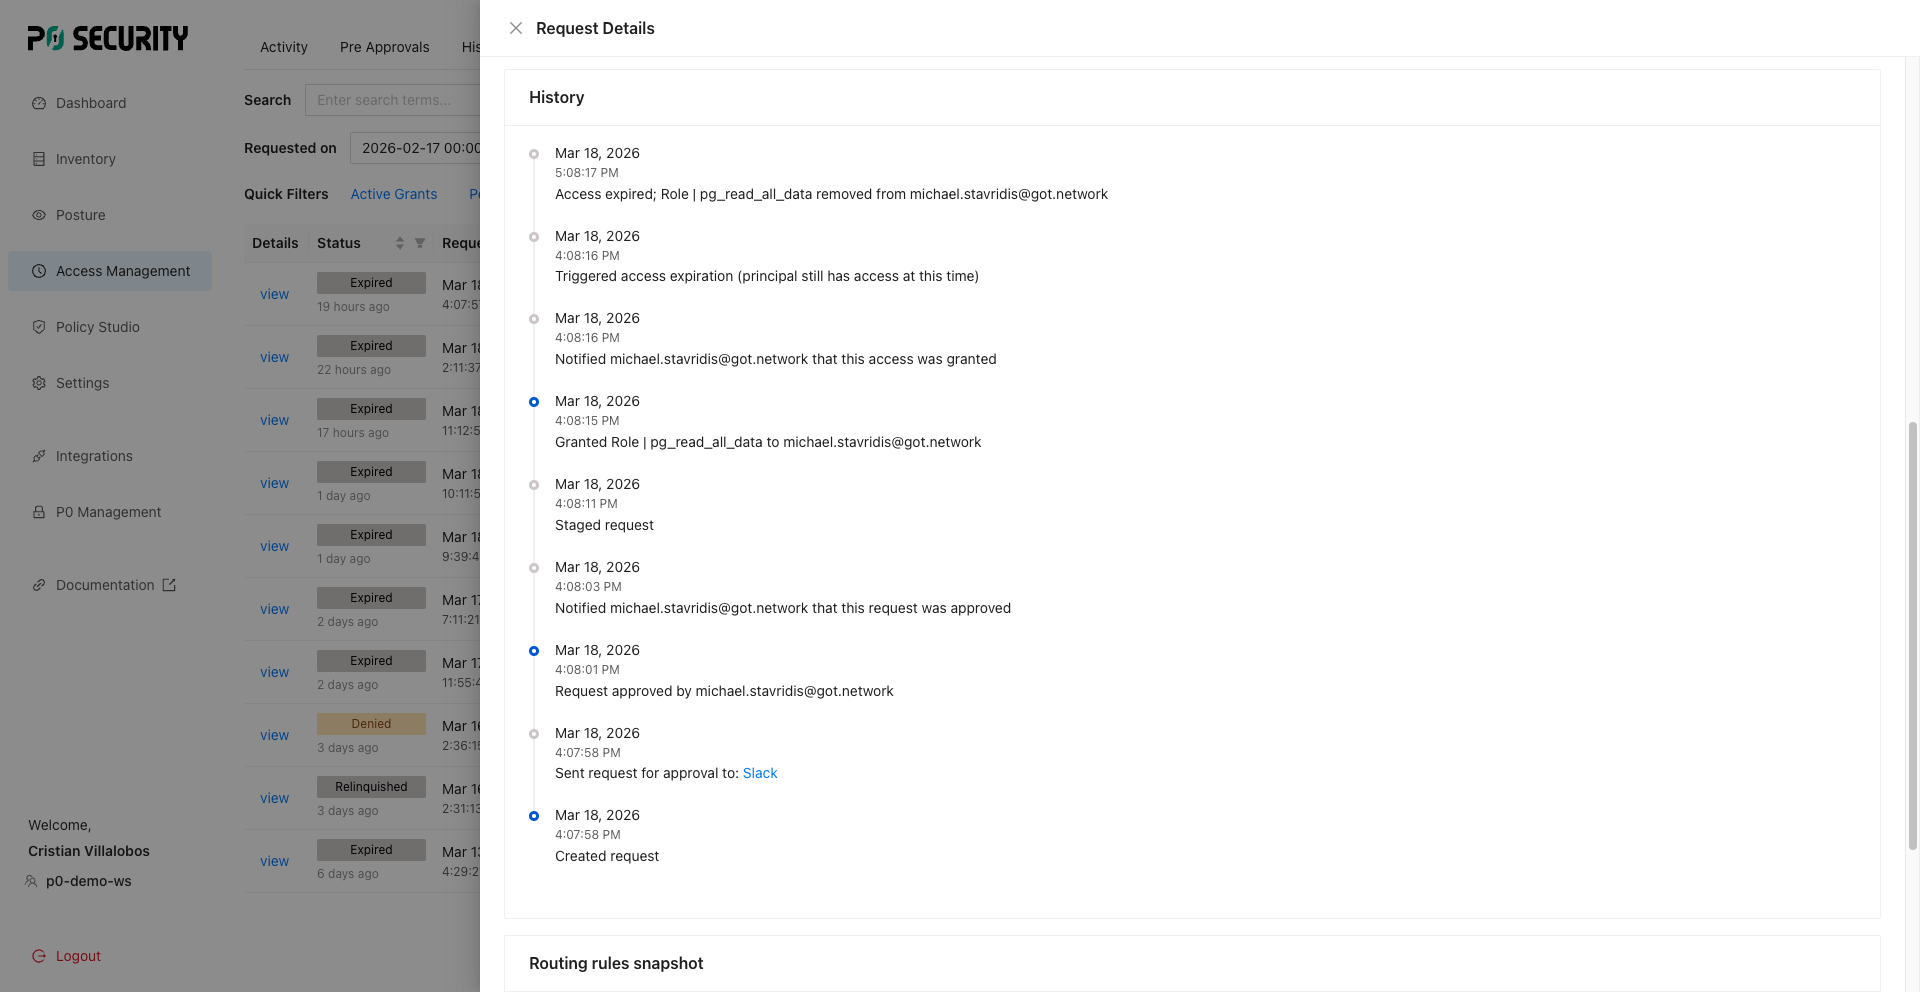
Tie every session to a verified IdP identity, eliminating shared accounts and static credentials while making every access action attributable and auditable.
Runtime policy enforcement
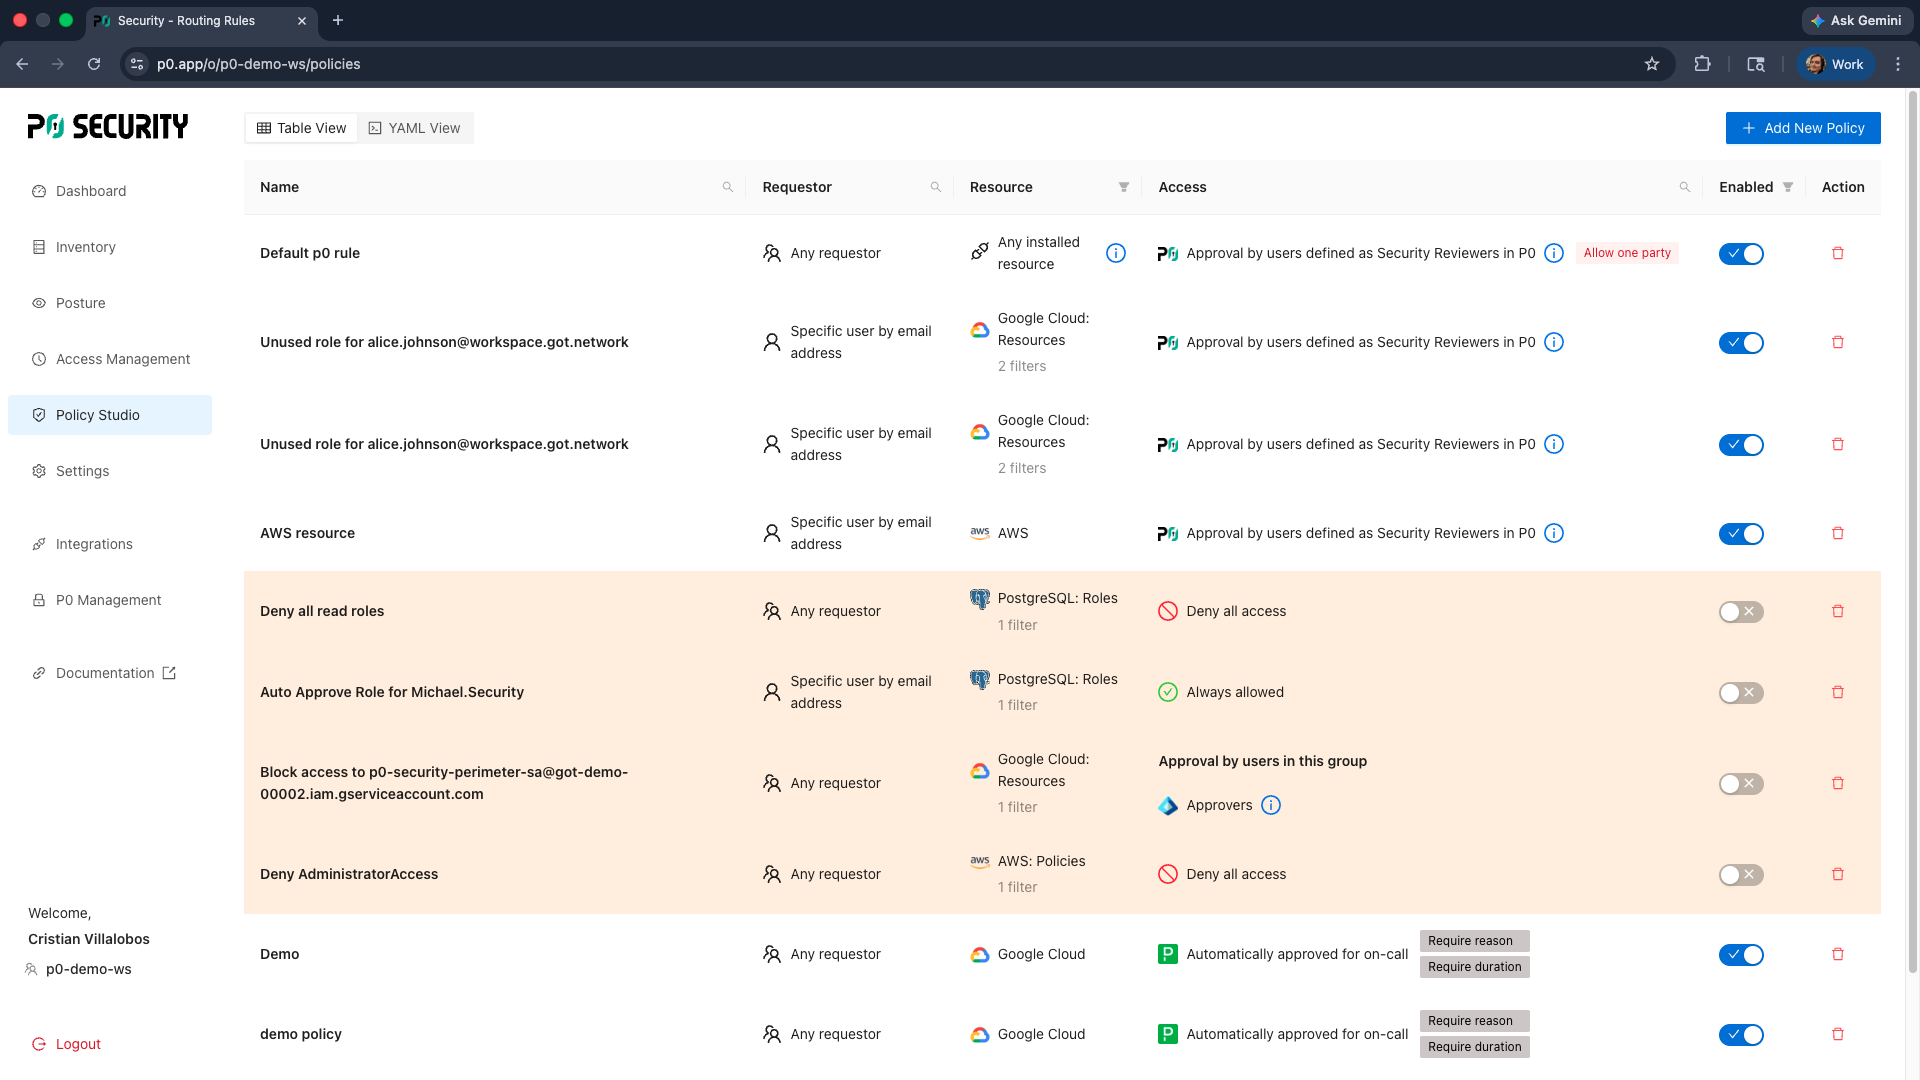
Automate JIT access using the policies and access controls you already have, provisioning only the privilege required and removing it when the work is done.
Built for the way developers work
Let developers request access through the systems and ChatOps workflows they already use, get approved faster and connect directly to native systems without managing keys or credentials.
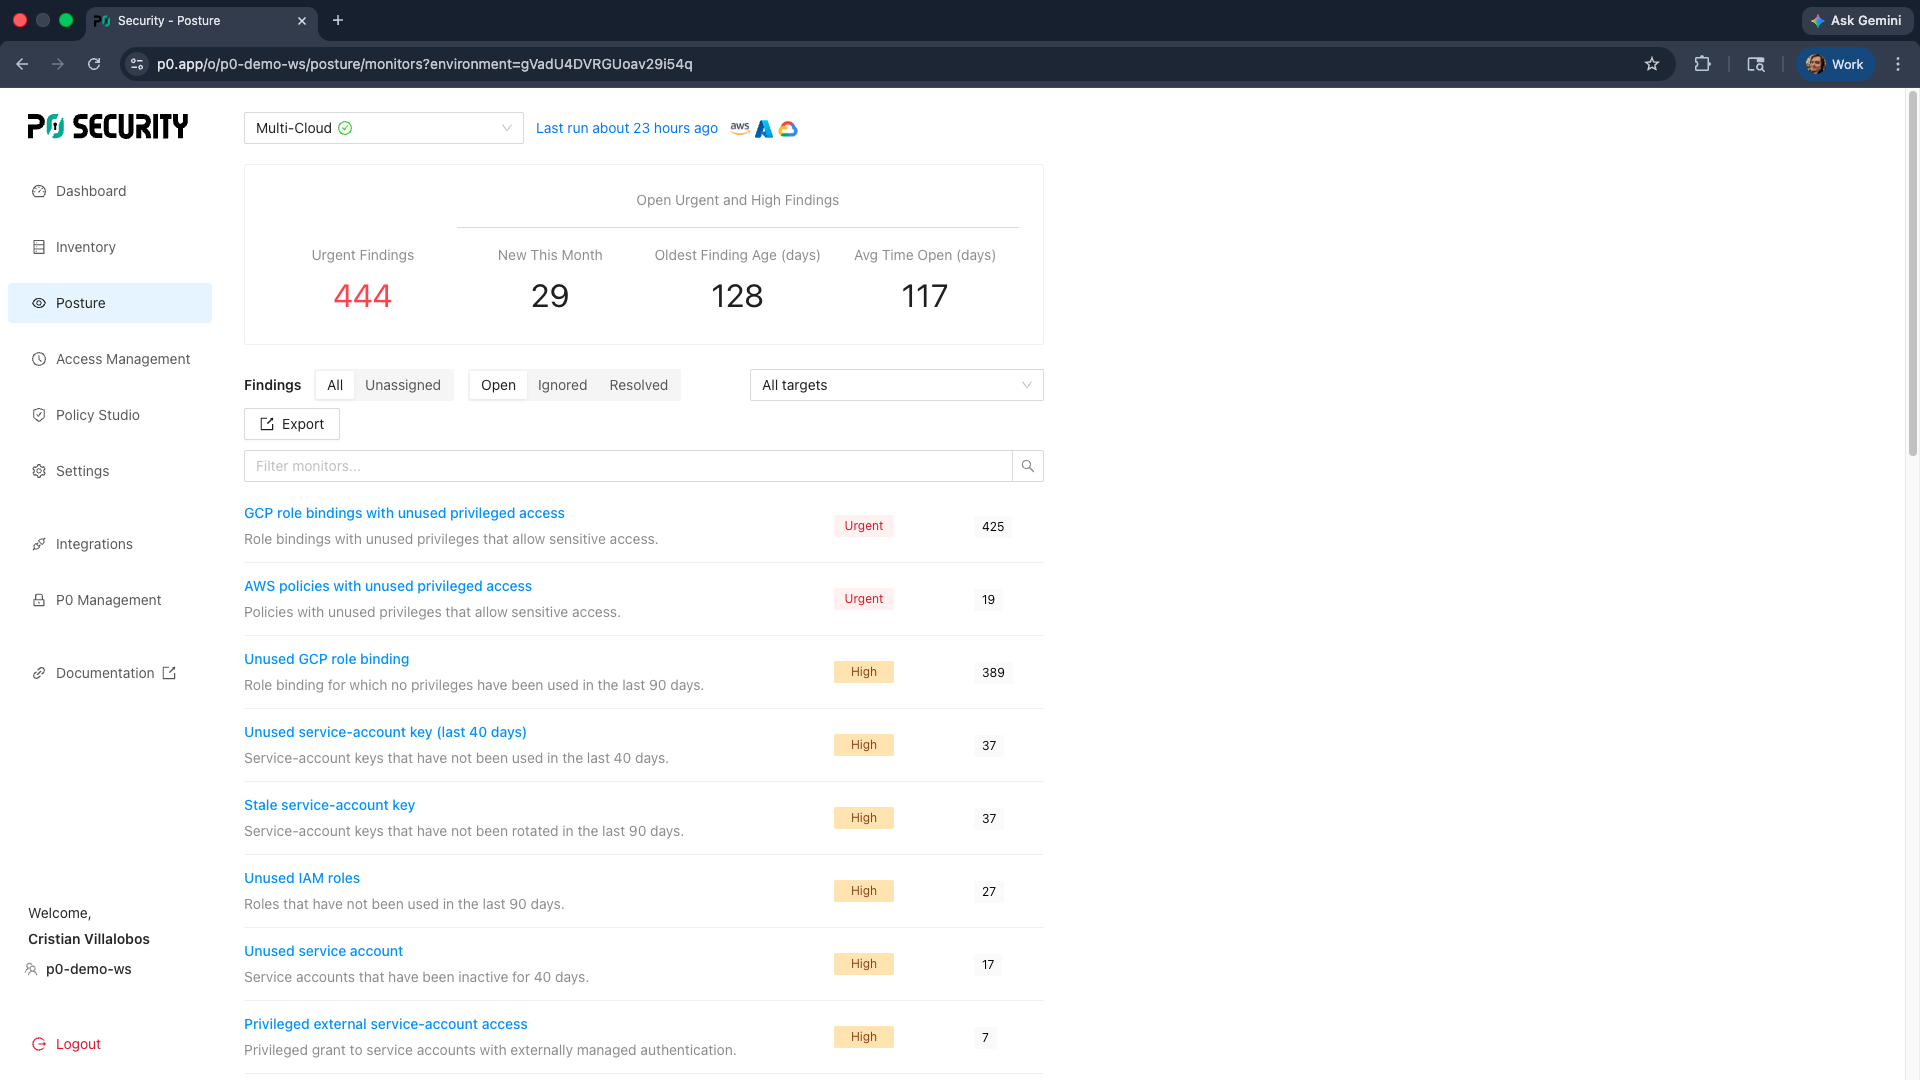
Here’s a quick look at five ways P0 helps you deliver least-privileged access for developers and other users.

“As leaders in enterprise AI, Resolve AI sees security as a core responsibility. As we transform how engineering teams manage and run production systems with our AI SRE, P0 Security delivers us just-in-time access that’s both secure and easy to use. Its deep coverage of our production environment with continuous audit trails have made P0 our standard for access management, centralizing control and streamlining security reviews.”
Madhu CS
Resolve AI
"P0 Security delivers us just-in-time access that’s both secure and easy to use.”