
Platform | Technology
The P0 Runtime Access platform
P0 discovers identity and privilege, applies policy and context and enforces least-privileged access at runtime across the systems where work actually happens.
Access has changed. Authorization has to change with it.
Sensitive systems are no longer accessed only by employees signing into applications. Developers connect directly to infrastructure. Workloads and service accounts operate continuously. AI agents act on behalf of users, machines and other agents.
That means an access decision may depend on more than a single identity. You may need to know who initiated the task, what identity is carrying it out, what action is being attempted, which resource is involved and what the surrounding context allows.
Traditional access controls were not designed to evaluate and enforce that full picture at runtime. The result is familiar: standing privilege, static credentials, fragmented policies and limited visibility into who or what actually acted.
P0 brings those decisions into one authorization control plane.
One control plane across every identity
P0 applies a common authorization model across the identities accessing your production environment, whether the actor is a person, a machine or an AI agent.
For agentic access, P0 preserves the relationship between the originator and the agent so policy can account for the full action chain, not just the credential presented at the target.
For human and machine access, P0 connects verified identity to policy and provisions the right privilege when it is needed.
Identity-first authorization
The platform behind runtime access control
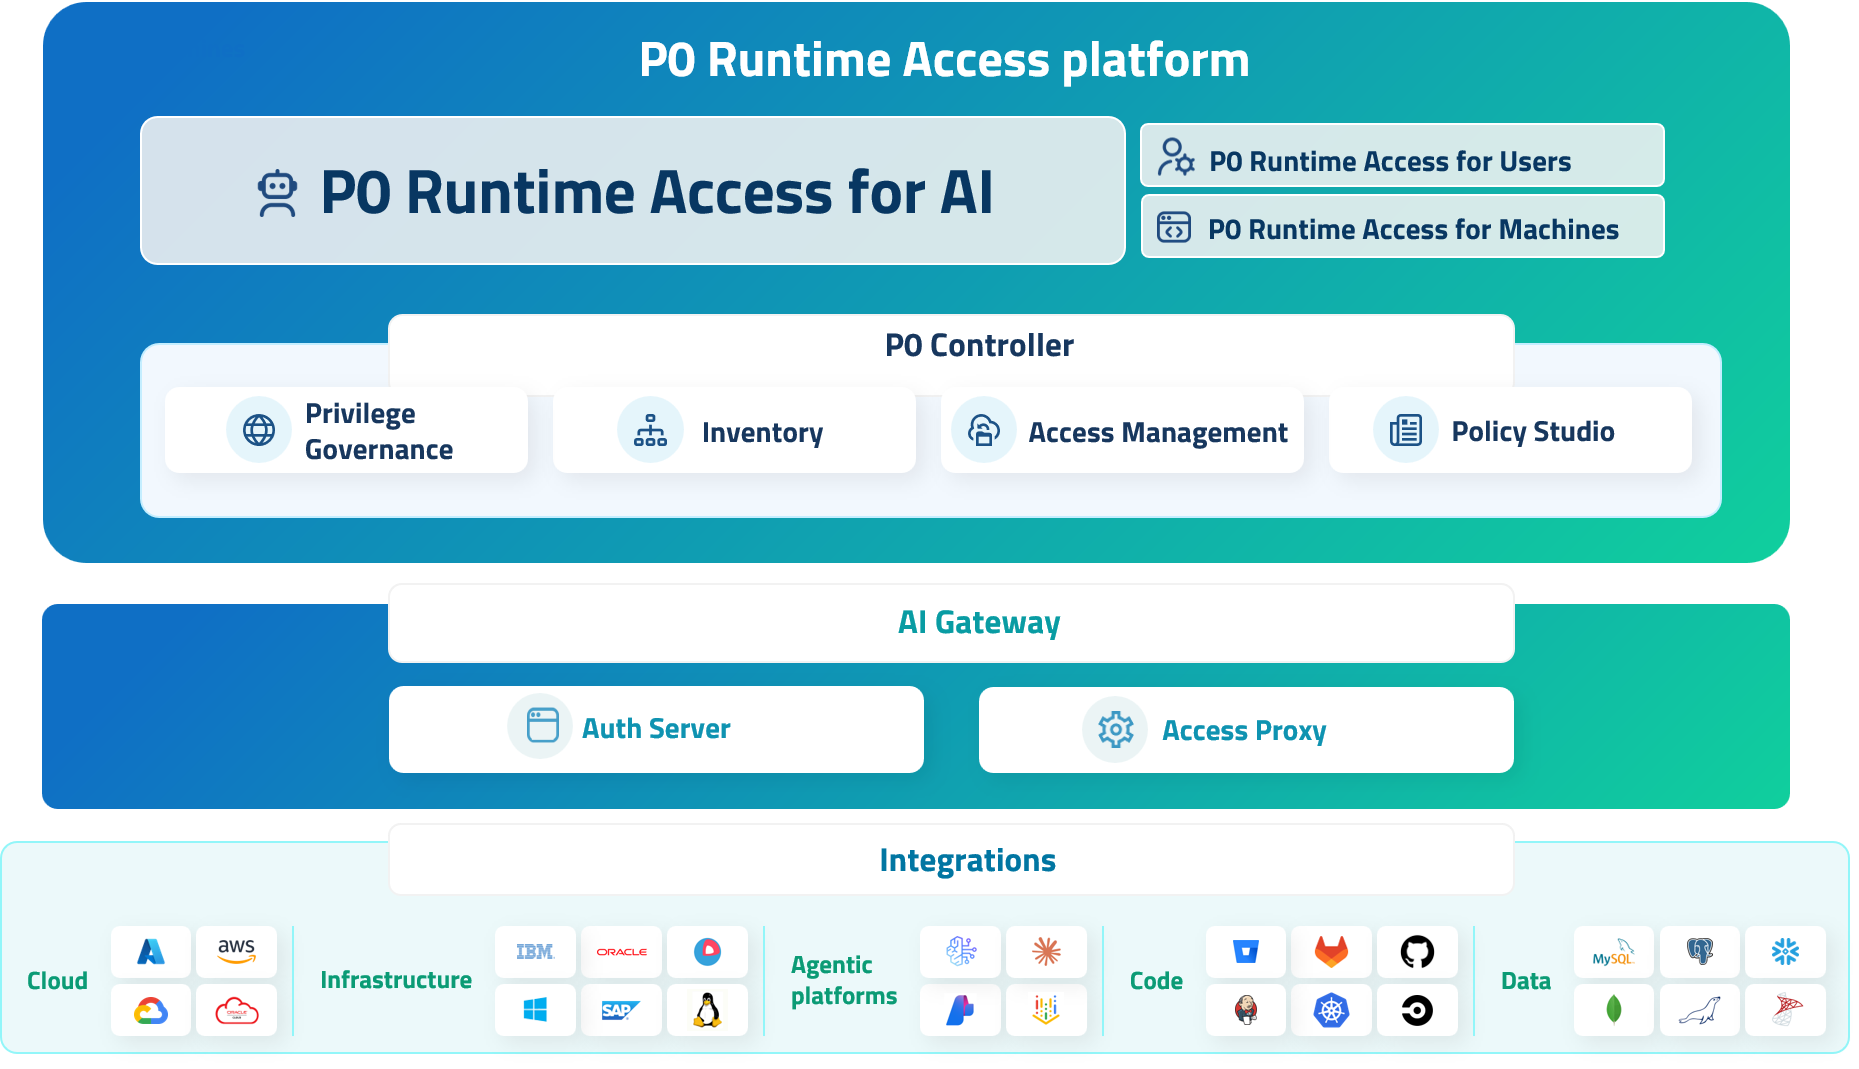
Runtime Access platform
Enforce policy when action happens
Evaluate access at runtime and allow, review or block sensitive actions based on identity, policy and context.
Provision only the privilege required for the task, then remove it when the work is done. Apply the same authorization foundation across users, NHIs and AI agents while preserving the additional context agentic workflows require.
Access Management
Provide access without risk
Automate how access is requested, approved, provisioned and removed.
Deliver scoped, just-in-time privilege through the workflows users already know while reducing standing access and static credentials.
Extend the PAM investments you already have with runtime access control built for cloud, SaaS and hybrid environments.
Privileged Governance
Turn privilege visibility into governed access
Bring privileged access under continuous governance by tracking entitlements, access paths, policy exceptions and privilege drift across users, machines and agents.
Preserve provenance behind access decisions and maintain the evidence needed to explain who or what had access, why it was allowed and whether it still should be.
Policy Studio
Turn your access rules into runtime policy
Define how access should be evaluated based on identity, resource, action and context, then apply those policies consistently across access workflows and environments.
For agentic access, extend policy to the blended identity and full action chain so decisions account for who initiated the task and what the agent is attempting to do.
Identity Inventory
Know every identity and where privilege exists
Continuously discover users, machines and AI agents along with their entitlements, relationships and access paths across connected systems.
Surface risky privilege, unmanaged access and identity relationships before they become a larger access problem.
Connector Library
Extend runtime control across systems you use
Connect P0 to cloud, SaaS, infrastructure, code, data and agentic platforms so identity context, policy and access controls can follow work across your environment.
Enforce decisions in the systems where access happens without requiring teams to rebuild the tools and workflows they already rely on.
The authorization layer for modern production access
The same authorization foundation P0 uses for humans and machines now extends to agents, with blended identity, full action-chain context and end-to-end policy enforcement.

Discover identities and what they do
P0 finds all AI agents, including shadow agents, the identities they use, the tools and systems they can reach and the privileges available to them.
Surface risky access paths before they become failures.
CAPABILITIES
- Agent, user and machine identity discovery
- Identity and privilege inventory
- Access path visibility

Control every action at runtime
P0 evaluates each requested action using the context behind it, including the originator, the agent, the task, the action and the resource.
Grant only the privilege required for the approved action, when it is needed, for as long as it is needed.
CAPABILITIES
- Runtime authorization
- Task-specific policy enforcement
- JIT entitlements

Prove what was done and why
P0 ensures a complete audit trail across the action chain. Connect the person or system that initiated the task, any agents involved, the identity used, the action attempted, the target resource, the policy decision and the final outcome.
CAPABILITIES
- Full action-chain logging
- Originator-to-agent attribution
- Policy decision and action history
P0 Security manages the entire privilege lifecycle in order to deliver secure and auditable access at developer speed. As the Runtime Access platform for modern production environments, P0 centralizes governance and enforces just-enough privilege and just-in-time access across every sensitive system, for every identity.
Zero standing privilege. Zero added friction. Because secure production access is Priority Zero™.
"Exceeded all my expectations."
"Temporary access used to be slow, manual, and buried in IAM group sprawl. With P0, we grant secure, fine-grained permissions in real time through Slack or CLI, using workflows that match how our engineers actually work. It’s fast, flexible, and lets us move lean and stay compliant without the usual overhead."
Johnny Chen
DevSecOps Engineer and InfoSec Manager, Finix
Dynamic access management
Access when it's needed. Gone when it's not.
Enforce ephemeral, scoped access exactly when it’s needed with context-based authorization that minimizes the identity attack surface.
Guides, how-to's and best practices.
From real-world customer stories to expert insights and product updates...everything you need to research and evaluate cloud identity.