
Platform | Technology
Runtime Access platform for AI
Enforce authorization across the full agentic action chain, preserving originator and agent context, applying policy at runtime natively in the target system and controlling access all the way into sensitive systems, tools and data.
A new approach to agentic access control
P0’s Runtime Access platform for AI is an authorization-native architecture built for agentic systems, where a single task can span multiple identities, agents, tools and target systems.
It connects identity, policy, runtime enforcement and target-system access across the full action chain to solve three requirements traditional access models were not designed for: preserve the identity and provenance behind every action, enforce what an agent can do at runtime and provision task-specific, short-lived access only when it is needed. Rather than treating authentication, gateway enforcement and downstream privilege as separate controls, P0 brings them into one authorization model that governs the action from originator to outcome.
Inside the Runtime Access platform for AI
The platform separates centralized identity and policy management from runtime enforcement in the customer environment.
The components below work together to establish identity context, evaluate policy, enforce authorization and control upstream access across the agentic action chain.
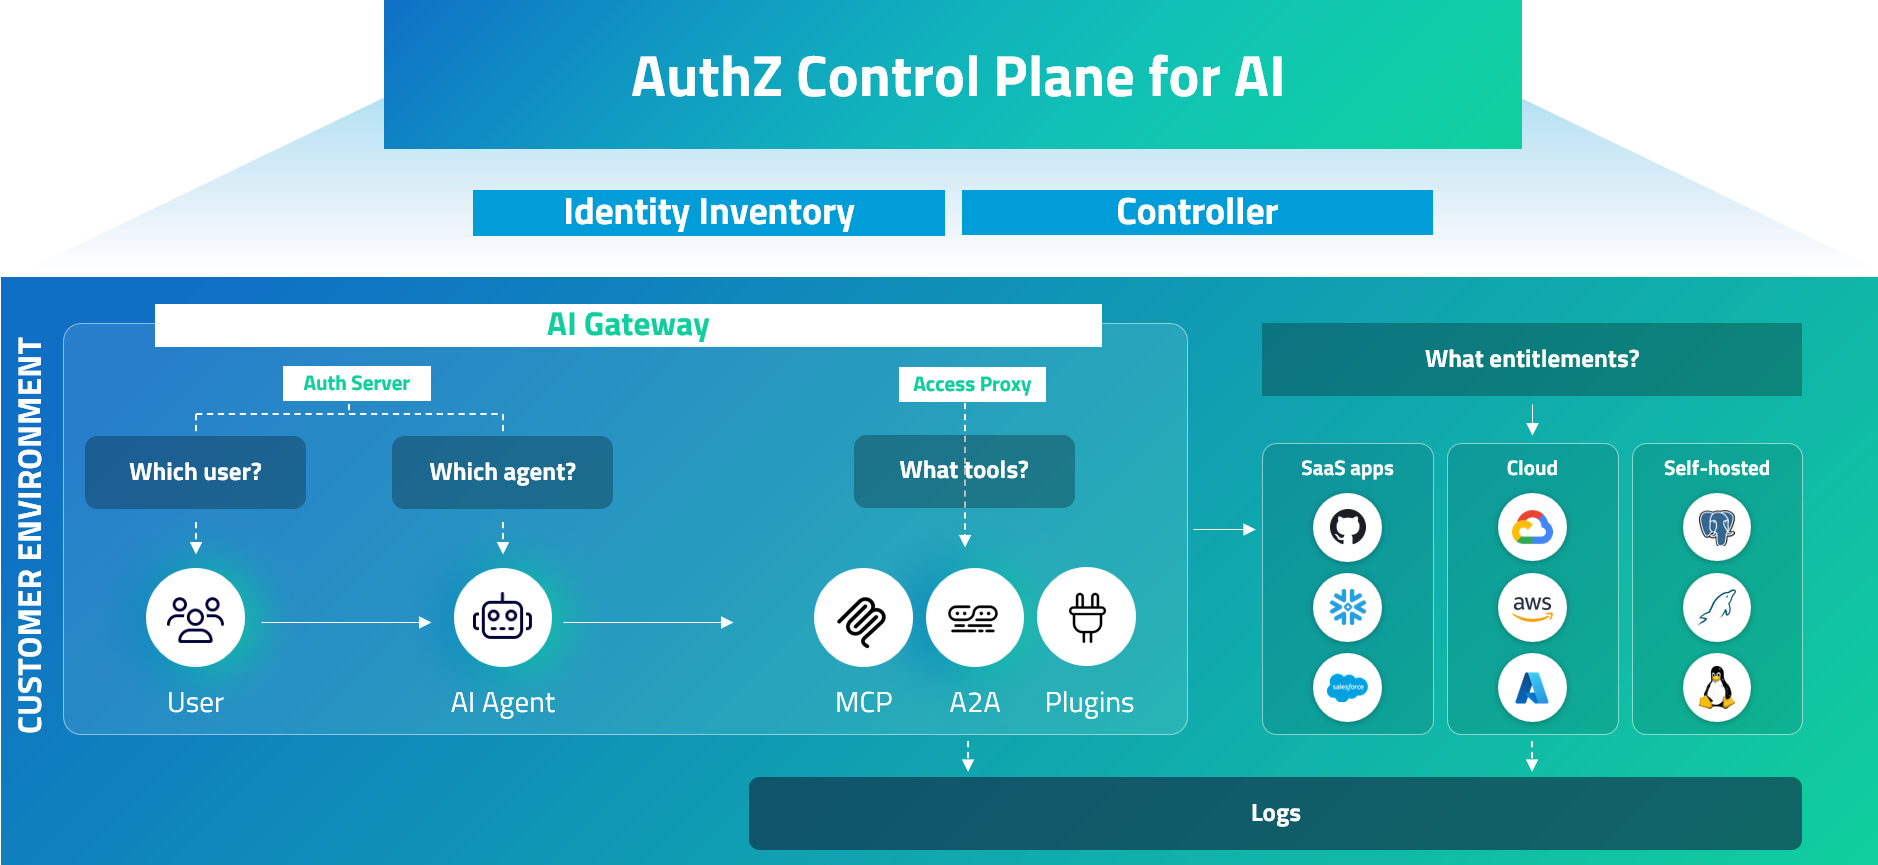
One control plane. Two deployment layers.
P0 combines centralized identity and policy management with runtime enforcement inside your environment.
P0 SaaS components
P0 SaaS provides the centralized identity, policy and control layer across agents, users and machines. It combines continuous identity and access discovery with centralized policy management, giving P0 a shared view of who and what has access, how that access is granted and the policies that govern what each identity can do. It contains two services: Identity Inventory and the Controller.
Identity Inventory
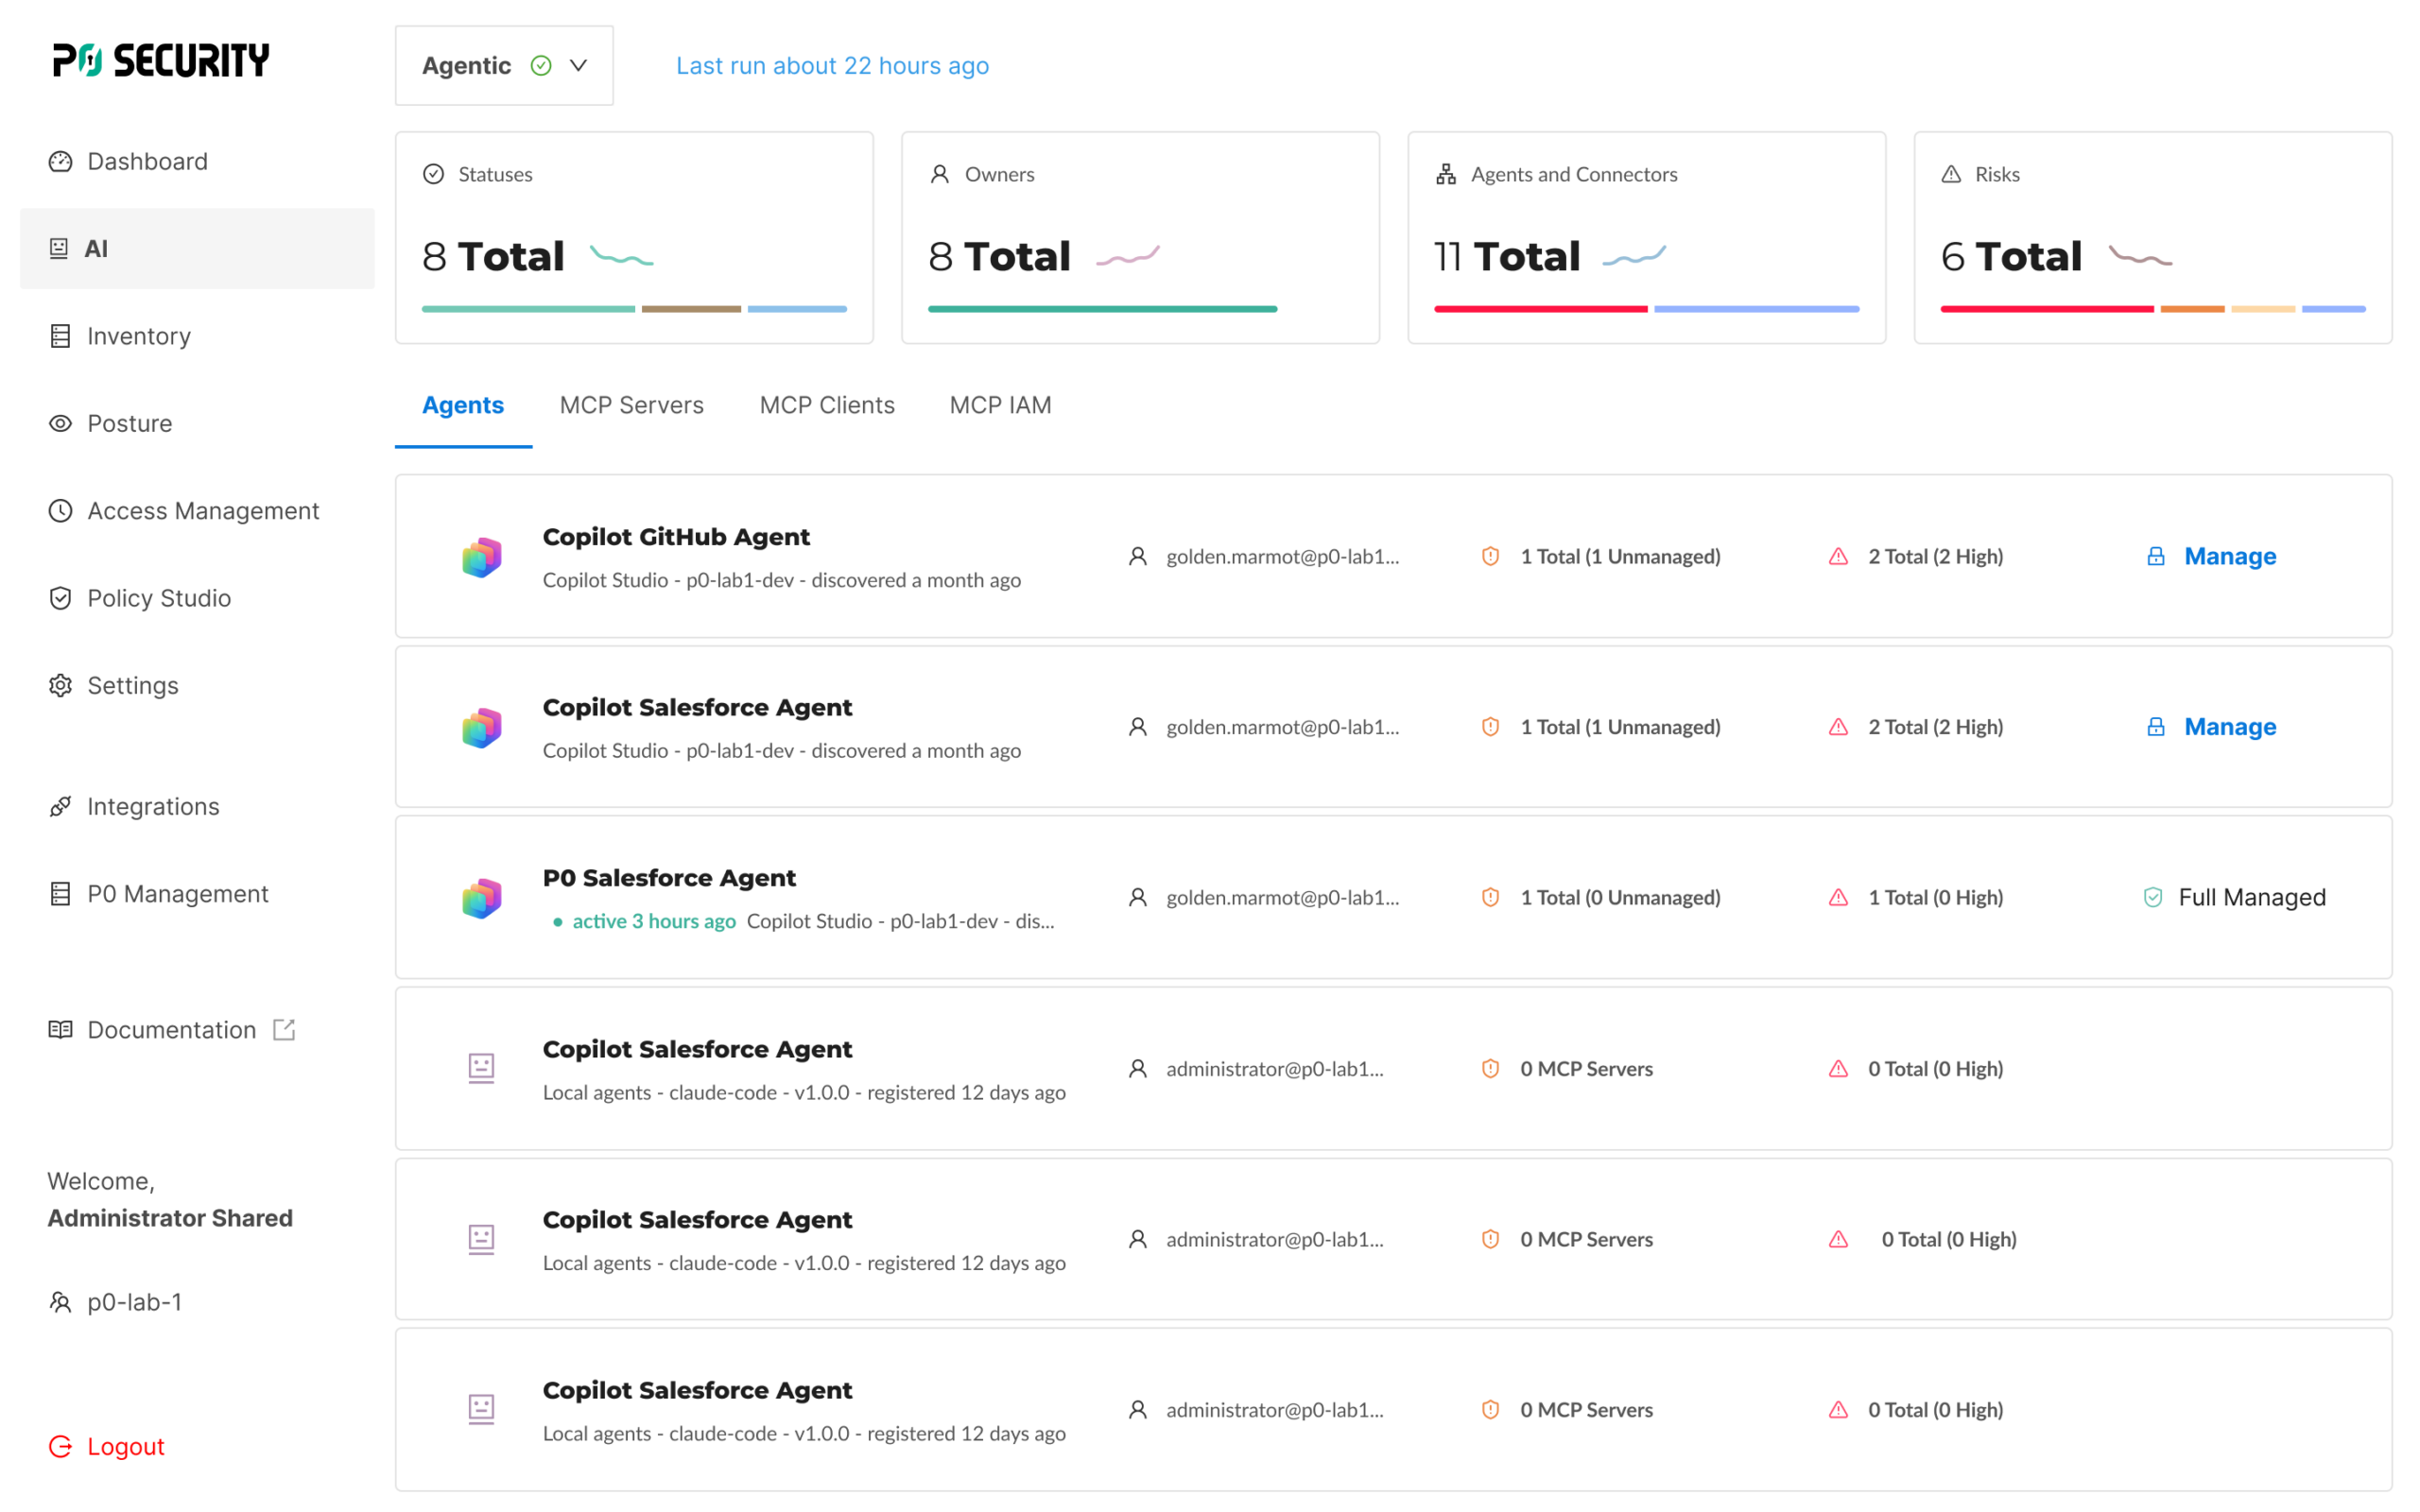
Continuously discover agents, MCP servers, users and machines along with the privileges, access paths and identity relationships behind them.
Surface shadow agents, standing access, ownership gaps and risky connections before they become runtime authorization problems.
Controller
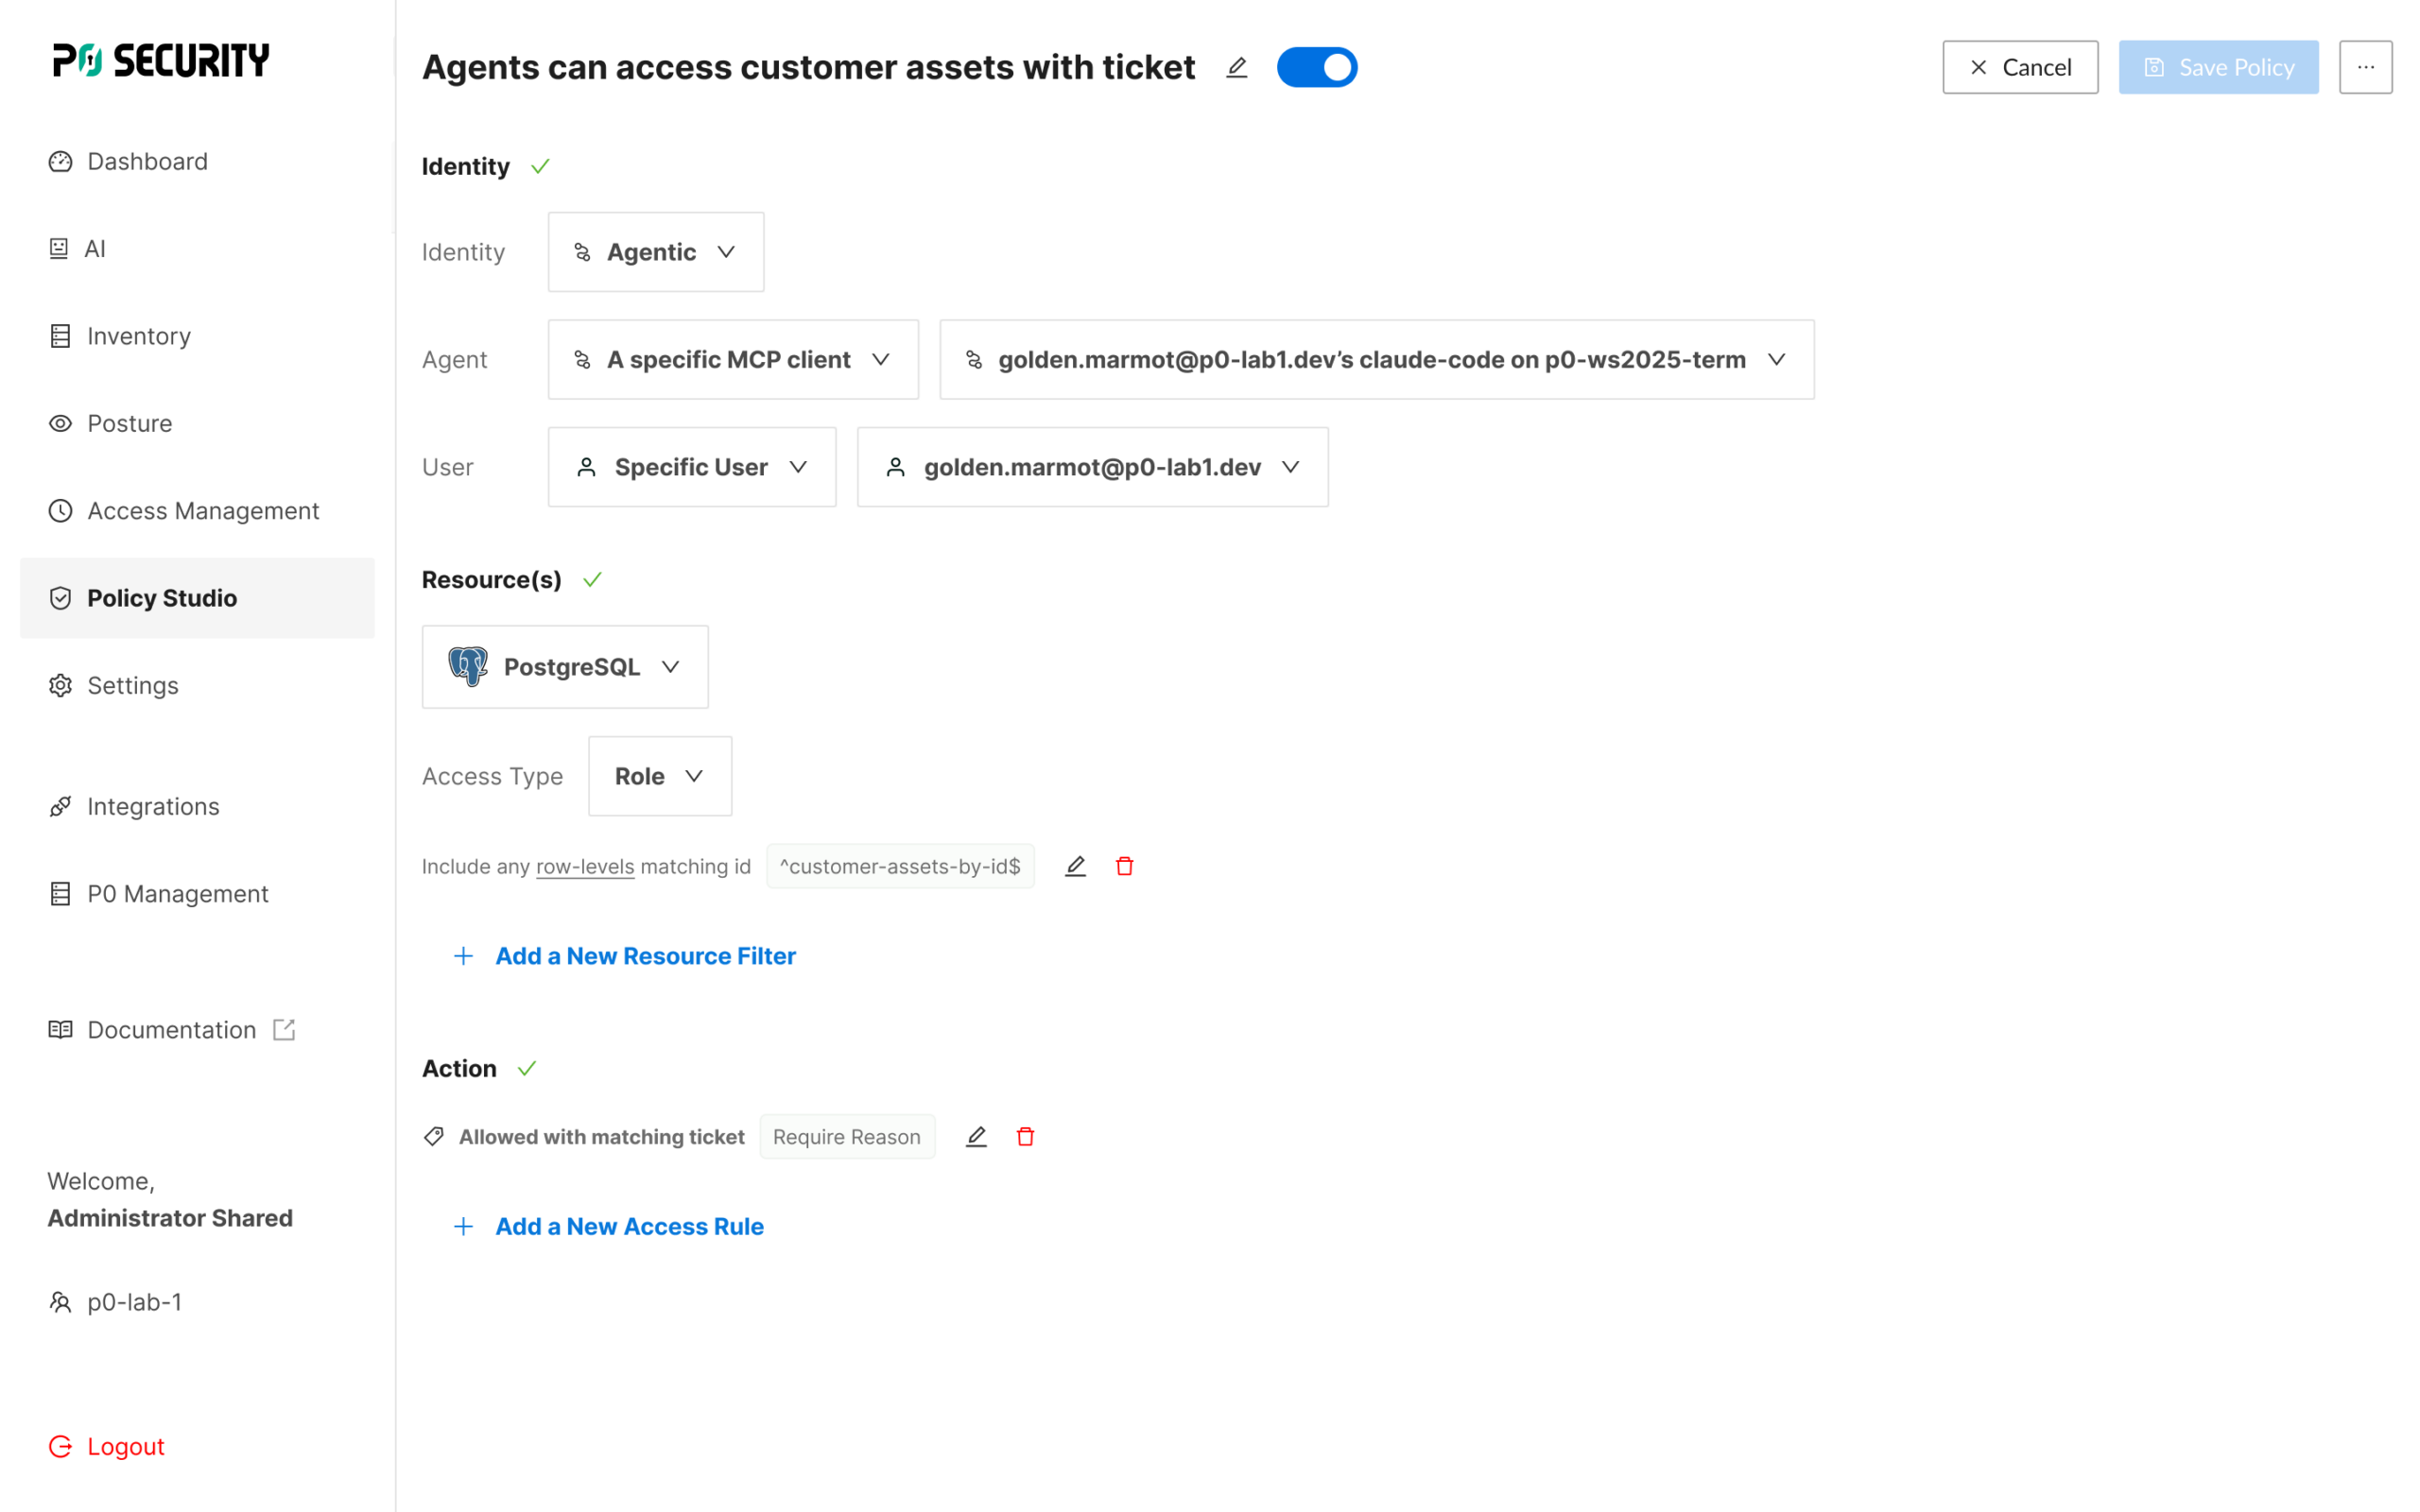
Define and manage agentic access policy, roles, approvals, server definitions and runtime decisions from P0 SaaS.
The Controller distributes configuration to the customer environment and coordinates the access request, approval, grant and revoke lifecycle.
P0 AI Gateway
The AI Gateway runs inside your environment and provides the runtime enforcement layer between agents, tools and upstream systems. Deploy the AI Gateway using a batteries-included Helm chart with required dependencies, a basic Helm chart that integrates with your existing infrastructure or a Terraform module for infrastructure-as-code deployment. P0 currently supports deployment on EKS, GKE and AKS. It includes two critical components: Auth Server and Access Proxy.
Auth Server
Federates with the enterprise IdP and establishes the identity and delegated context behind the request.
The Auth Server binds the originator and acting agent to the request and can exchange short-lived upstream credentials when approved access requires target-system privilege.
Access Proxy
Intercepts governed tool calls before they reach the downstream MCP server, API or workflow.
The Access Proxy maps inbound identity and session context to ephemeral credentials and permissions, allowing the target system to enforce authorization using its native controls.
One architecture across every identity type
Regardless of how the task begins, P0 creates a blended identity that preserves the originator, acting agent and delegated context together, so downstream actions can be evaluated against the original task and authorized scope.
Human-to-agent
A user invokes an agent or copilot to perform a task on their behalf.
Agent-to-agent
A downstream agent delegates part of a task to another agent.
Machine-to-agent
A workload, application, service, scheduler or event activates an agent without human involvement.
How a governed request moves through P0
Establish identity and delegated context
The Auth Server federates with the enterprise IdP and establishes the originator, acting agent and session ID of the task.
Bind context to the request
The signed JSON Web Token issued by the Auth Server (JWT) carries the necessary claims to establish the delegation chain: sub, nested act, sid, along with other standard claims.
Receive access requests
The P0 Access Proxy receives an access request from the Agent for the specific task, formulated in the native IAM of the target system (e.g. a role).
Evaluate authorization
The P0 Controller evaluates the request using identity, delegation chain, task, tool, target and current conditions.
Apply the policy decision
The action can be allowed, denied, limited or escalated for approval by the P0 Controller based on what is authorized at that moment.
Provision access lease in target system
The P0 Controller safely creates an ephemeral identity with the approved permissions in the upstream system and makes its credentials available to the P0 Access Proxy.
Intercept the proposed action
The Access Proxy receives the governed tool call, tied to the access lease, before it reaches the upstream system.
Forward the authorized action
The Access Proxy re-verifies the lease and re-evaluates authorization before proceeding with the upstream tool call using the the ephemeral identity and permissions mapped to this lease.
Record the result
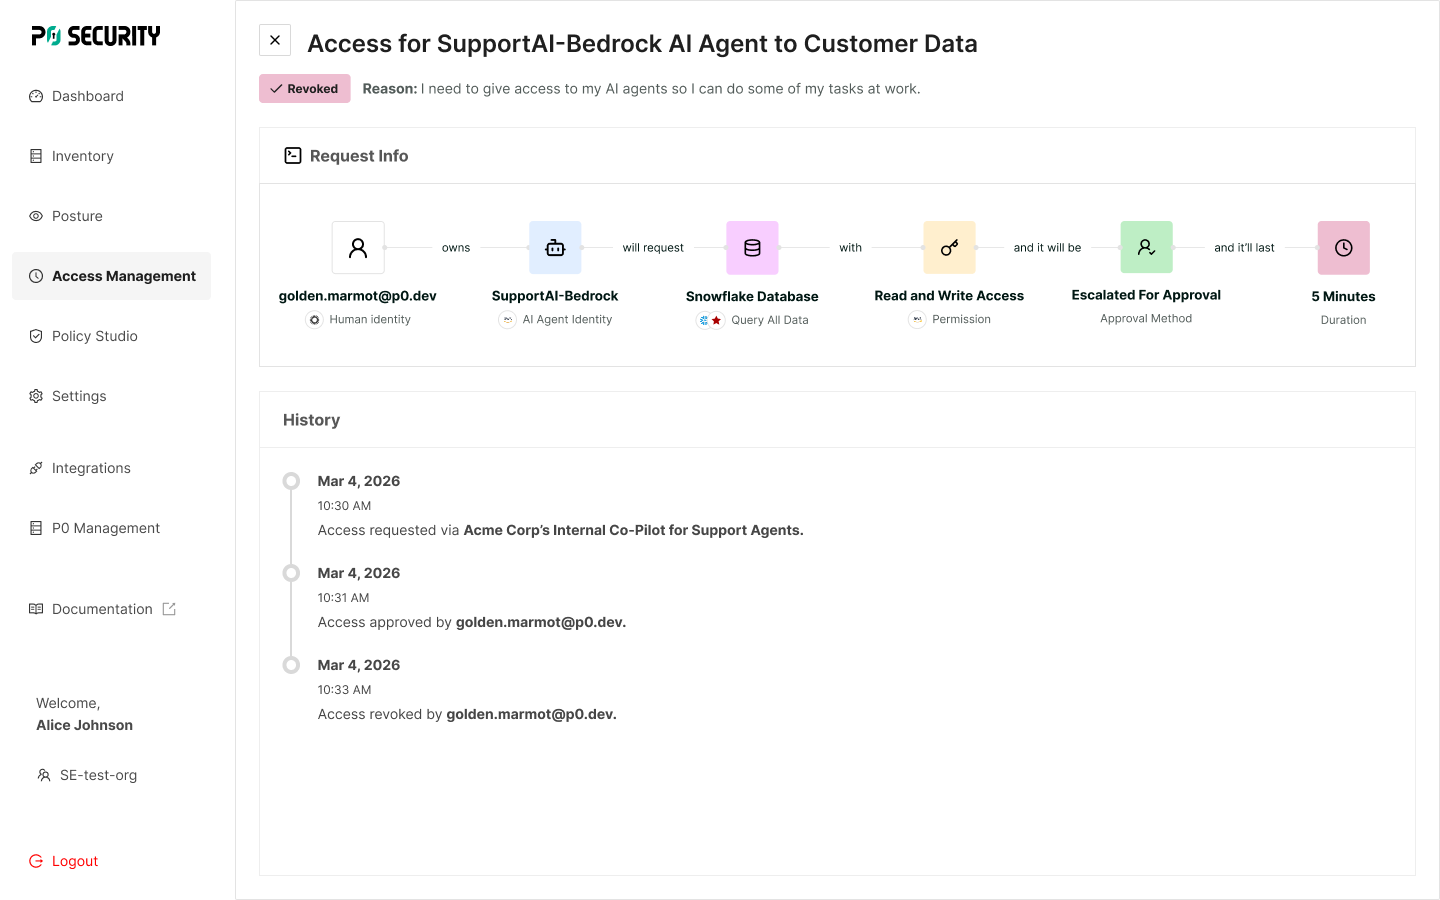
P0 captures the identity, policy, approval, action, target and outcome for logging, audit and investigation.
Enforce every step, not just the gateway
Authorization has to hold across the full action chain. P0 evaluates what the agent is trying to do, then extends that decision into the upstream system when the task requires actual privilege.
End-to-end authorization
Runtime authorization does not end when a tool call passes through the gateway.
P0 can enforce access at two different points in the action chain.
Action-level enforcement
Control whether the proposed tool call or operation is allowed to proceed.
The Access Proxy evaluates the request against policy using the identity, delegated context, task, target and current conditions surrounding the action.
Target-system enforcement
Control the actual privilege available inside supported downstream systems.
When access is required, P0 provisions short-lived access for the task and revokes it when the task or approval window ends.
Preserve the complete action record
Every governed action should be explainable after the fact.
P0 connects the full sequence behind the action, preserving the originator, acting agent, task context, policy decision, approval, privilege granted, tool used, target system and resulting outcome.
That gives security and operations teams a complete record of not just what happened, but why it was allowed, which identities were involved and what access was actually used.
Audit activity can be sent to your logging destination or SIEM so the full authorization trail remains available for investigation, compliance and review.
Apply the same control plane across every use case
The same runtime architecture can govern agentic workflows with very different originators, tools and access requirements.
Coding and SRE agents - control repository, CI/CD and production actions while keeping high-risk changes inside approved scope.
Cost optimization agents - allow discovery and analysis while gating infrastructure changes behind policy and approval.
Admin and support agents - preserve the originating user context while controlling read, write and destructive actions across support and administrative systems.
Agent-to-agent workflows - carry identity, delegation chain thrwugh upstream agents so each handoff remains governed and attributable.
Policy evaluation context
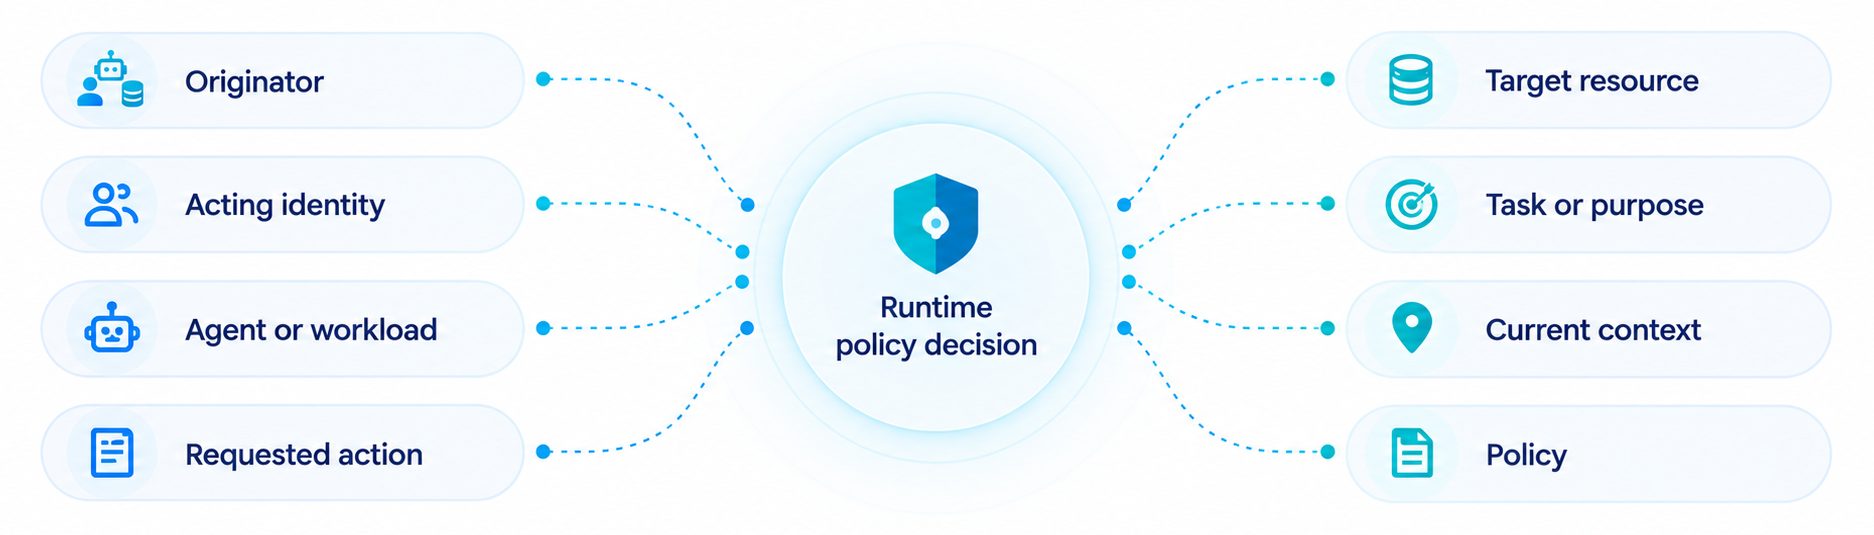
At runtime, P0 evaluates the proposed action using the full context associated with the request.
That includes the originator, acting identity, agent or workload, requested action, target resource, task or purpose, current conditions and the policy that governs whether the action is allowed.
P0 evaluates these inputs together before the access lease is provisioned and again before the governed action is allowed to proceed.
“Claude Code is reshaping our access risk model. Engineers could use agents to automate scripts on remote servers or access sensitive data on production databases.
One unintended command, rm–rf or mkfs, executed with an engineer's authority, can have catastrophic consequences. Every agent action needs to be evaluated against policy at runtime, not after the fact.”
Venkat Venkatraju
Cloud Security Engineer at Splunk
“Every agent action needs to be evaluated against policy at runtime, not after the fact.”