
Another day, another incident. This time, at Fireworks AI. The entire summary is worth reading, if you haven’t already done so. (Link in the comments)
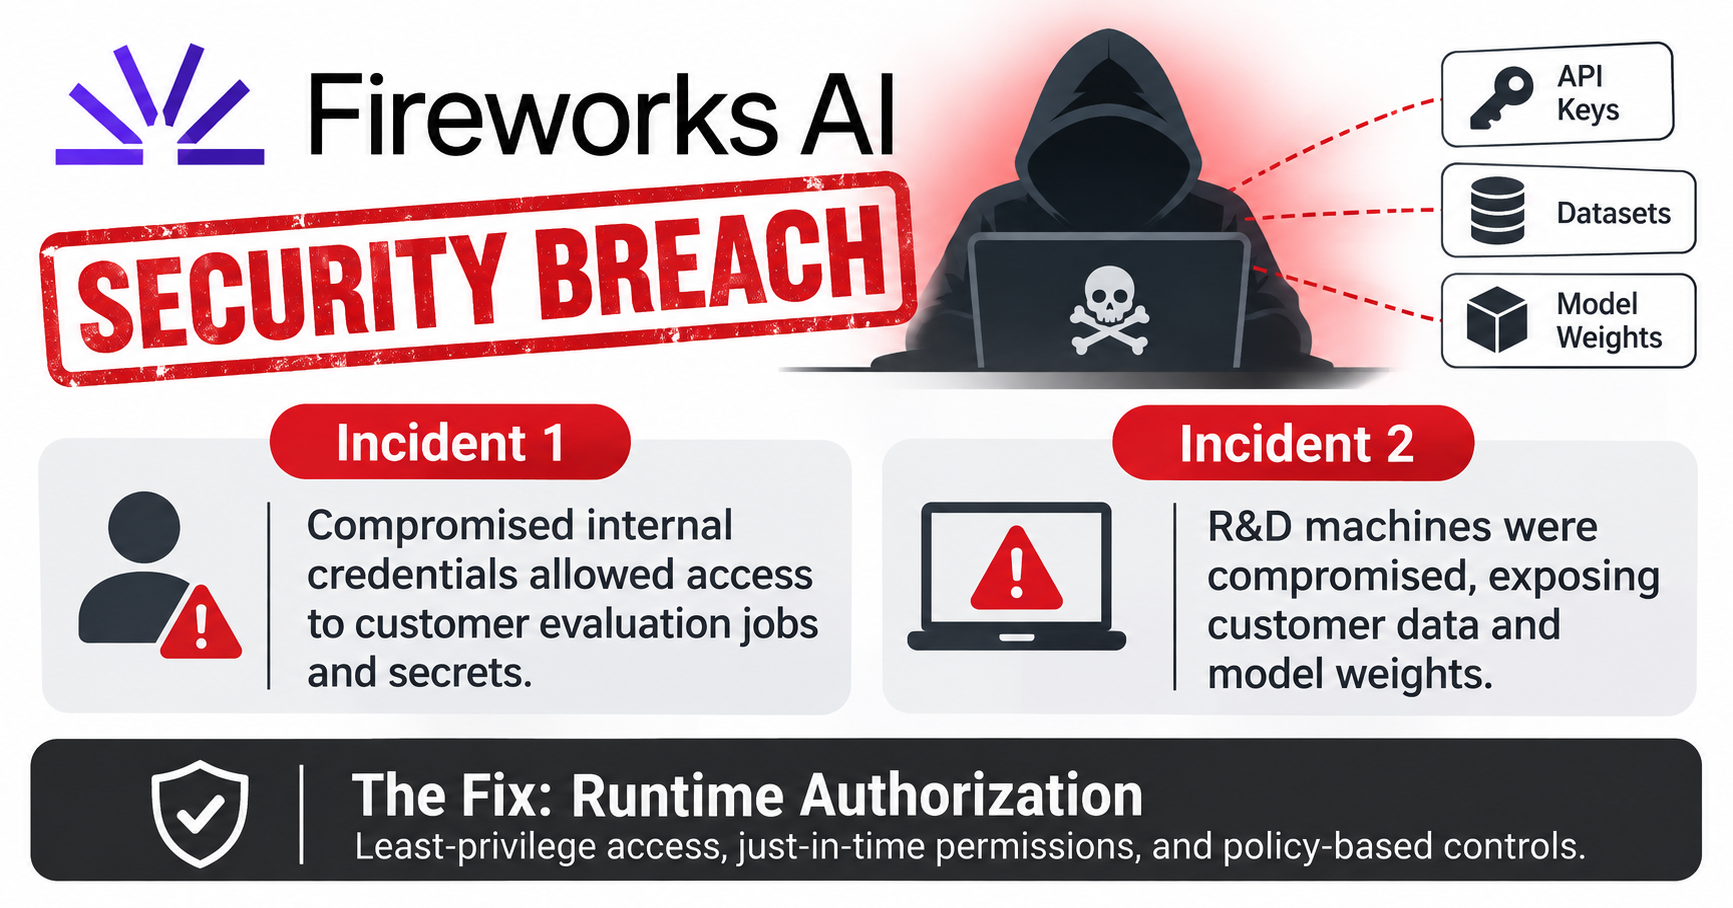
TLDR: Fireworks AI suffered not one, but TWO security breaches last month, exposing customer API keys, datasets, and partial model weights.
First breach: Attackers used compromised internal credentials to access customer evaluation jobs and steal secrets stored in environment variables.
Second breach: Attackers compromised R&D machines through a CSP (AWS? GCP? Neocloud?), executed unauthorized workloads, and accessed customer data and model weights.
None of this is new. All of it underscores how important the fundamentals are today.
Finally, I asked AI how these breaches could have been prevented (emphasis my own).
First breach: Stolen Fireworks employee API keys or internal service-account tokens could have been rendered useless through least-privilege, just-in-time authorization restricting access to customer evaluation jobs and their secrets.
Second breach: Compromised R&D machines could have been prevented from accessing customer datasets and model weights by restricting their AWS IAM roles, GCP service accounts, or Kubernetes service accounts to development resources, with no standing access to production.
In other words, RUNTIME AUTHORIZATION.
Repeat after me: NHIs are a feature. JIT is a feature. Identity security = RUNTIME AUTHORIZATION, based on policy.
A bit like P0 Security.