
Privileged Access (PAM)
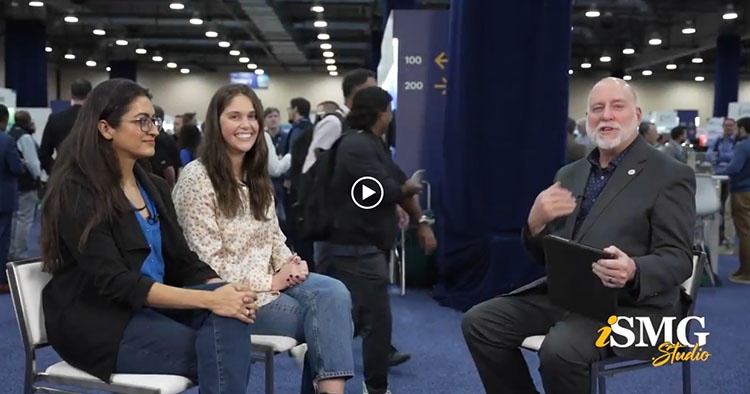
When Neha and Kelsey said the quiet part out loud about privileged access
Agentic systems are accelerating everything. They increase the number of access paths, expand the impact of bad permissions and highlight the limits of tools built for manual control.
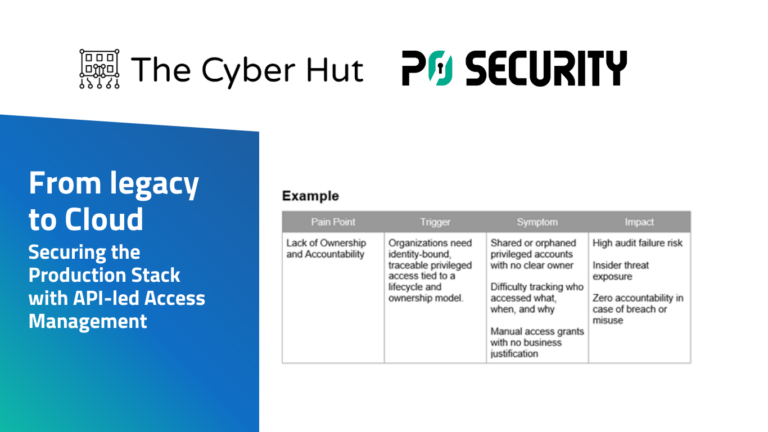
From Legacy to Cloud: Securing the Production Stack with API-led Access Management
By Simon Moffat
This is the final of a three-part series taking a look at modern privileged access management and how its evolution to the protection of more systems and more identities leads to both security and productivity improvements.
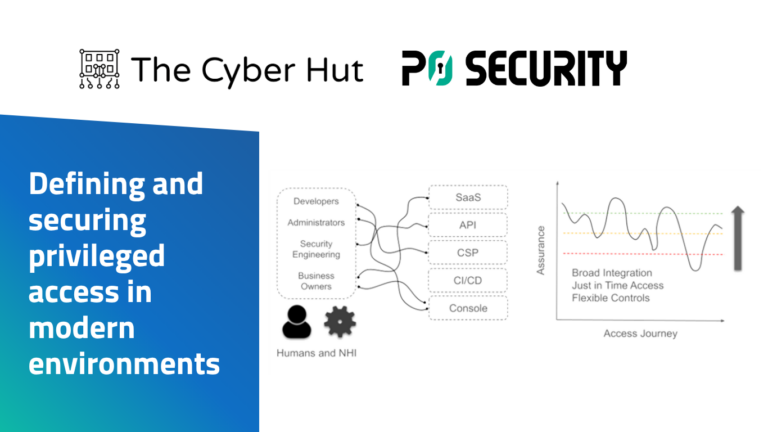
Defining and securing privileged access in modern environments
By Simon Moffat
Today’s privileged access challenges demand a shift from static, siloed controls to identity-centric, Just-in-Time (JIT) models that improve security while accelerating deployment and engineering workflows.

Why PAM Needs to Evolve
By Simon Moffat
Modern-PAM needs to support more systems, more accounts, a hybrid deployment landscape and have the functionality available to a broader array of integrating technologies via modular, composable and API-first capabilities.

The rise of non-human identities and the future of PAM
Learn how security teams can evolve identity programs to manage risk, reduce exposure paths, and prepare for the next wave of AI-driven access.

Why cloud-native demands an API-led approach to PAM
Learn why vaults and jump servers can’t keep up, and how an API-led model delivers just-in-time access, automates least privilege, and strengthens security without slowing developers down.

Why Enterprises Are Upgrading to Next-Gen PAM for Cloud Security
Enterprises upgrade to next-gen PAM for secure, agentless cloud access and compliance