
Just-in-time access
Why Authentication Is Not Enough For Agents
Logging can tell you something happened. But none of that alone determines whether the action should be allowed, given the full chain of authority behind it.
The three types of JIT (And why only one actually kills standing access)
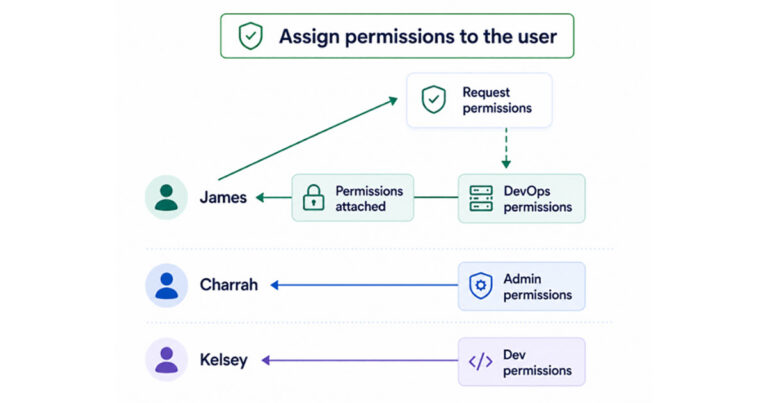
"Just in Time (JIT) access" is a simple concept but can be architected in multiple ways with significant tradeoffs. In this blog, we’ll break down the three major ways of achieving JIT, only one of which actually removes longstanding access altogether. These three types are: credential check-in/checkout timed group membership JIT permission assignment All three achieve some version of JIT, but only the latter removes the need for longstanding admin credentials altogether. In assessing these three approaches, the goals of JIT should be to: Reduce the number of users with unused sensitive permissions Reduce the risk of a compromised credential Improve user experience for complicated login flows Most approaches do something to reduce the number of unused permissions, but can lead to a false sense of security, as longstanding permissions switch to a role rather than a user account. Below […]
The identity risks of vibe coding
By Neha Duggal
Vibe coding changes the relationship between a developer and the code they ship. It does not change the fact that code carries identity and access decisions, and that those decisions have consequences.
More than visibility: P0 introduces privileged access control for agents
By Neha Duggal
AI agents are increasingly playing a part in how modern developer teams build, automate, and scale.

Security features for Kubernetes
P0’s Kubernetes integration grants temporary access to sensitive resou…