
A new threat vector emerges. And the first thing every security team wants is….visibility.
Some vendors call it governance, others say observability or discovery.
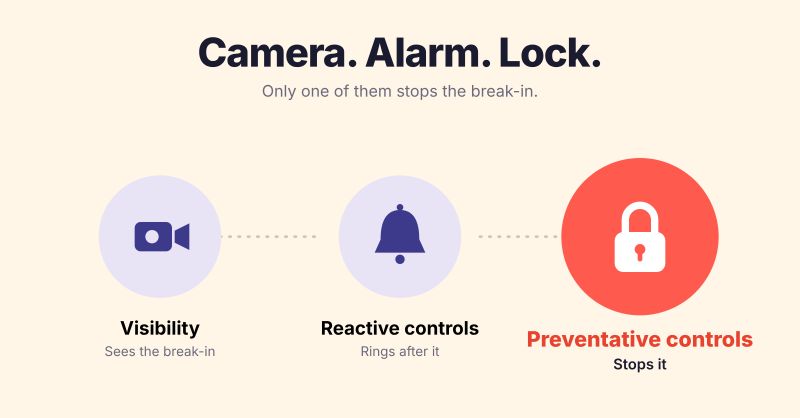
These days, 90%+ of my customer conversations about agentic security start with some variant of: “I have no idea what agents are out in the wild. I want visibility”
However, visibility is also the easiest problem to solve as a vendor. Point Claude Code at every agentic platform’s native APIs, build a graph, done. (OK, getting to production is a bit harder. But you get the point.)
But if it’s easy for you, it’s easy for EVERY other security vendor. Visibility gets commoditized, and in a commoditized market, large incumbents win because they reach customers first.
The next frontier: reactive controls. like automated blocking and remediation. Take the visibility and automate the response. Classic detection and response, or “XDR.” Harder to build, but eventually, they get commoditized too.
And then, inevitably, customers ask for the holy grail: preventative controls. Because prevention is always better than cure.
These are also the hardest to get right. Why?
• Preventative controls sit in-line with business traffic. If a vendor goes down, business is interrupted, so the reliability bar is much higher.
• They touch many teams. Workflows change, so you need real buy-in from many teams across the organization.
• They are not solving a hair-on-fire problem, unlike reactive controls, which you need after the inevitable breach.
Still, it’s the gold standard security teams aspire to.
In agentic security, we’re now entering this wave. Nearly everyone offers visibility and governance. Many offer reactive controls. Very few offer prevention.
Over the next 12 months, this is where the market goes. It’s the only way to control the legions of agents coming online.
So….what are these preventative controls? Glad you asked! Let’s look at P0 Security:
• Runtime policy enforcement on which tools agents can call
• Task-scoped permissions across apps, provisioned only for the duration of the task
• A unique cryptographic identity per agent
Or in other words, the gold standard for agentic security: identity and access control for every agent.
#AgenticGovernance #AgenticIdentity #IAM #RuntimeAuthorization