

Gergely Danyi

Latest research and insights
Just-in-time ephemeral database access
The p0 approach to just-in-time ephemeral database access streamlines ...
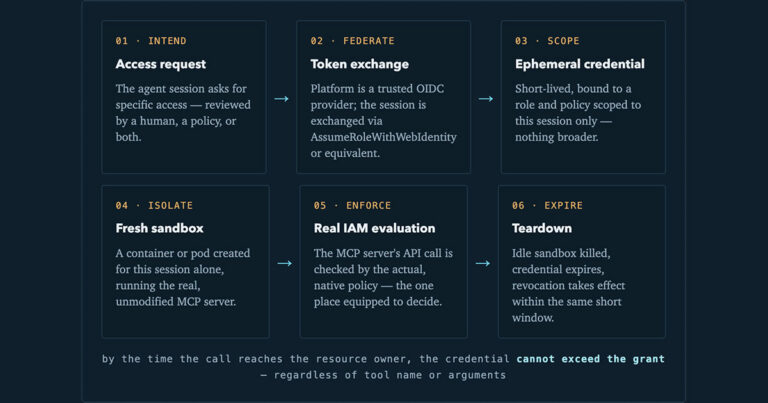
From MCP Tool Filtering to Runtime Access Control
Tool-level filtering alone is not access control.

Scalable user authentication for Kubernetes clusters with OpenID Connector
A real-world guide for setting up federated identity using OpenID Conn...

OAuth scopes don’t equal secure MCP authorization
OAuth scopes solve an important part of the authorization puzzle: delegated capability. But they are only one piece. To do MCP authorization properly, you need scopes for the big picture and server-side RBAC for least-privilege enforcement.
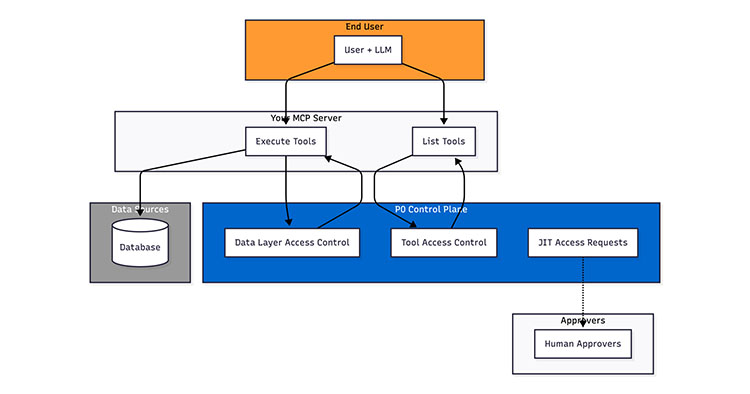
Technical Deep Dive: P0 Runtime Access for AI
The P0 Runtime Access for AI lets developer and security teams control access for agentic applications that connect to internal data sources, such as a Postgres, Snowflake, Mongo database through a chat interface.
The ServiceNow AI breach: Why agentic access requires layered defense
The ServiceNow breach is a wake-up call. As we deploy more autonomous agents with access to critical business systems, we need authorization architectures designed specifically for the agentic paradigm not retrofitted from traditional security models.

Security features for Kubernetes
P0's Kubernetes integration grants temporary access to sensitive resou...