
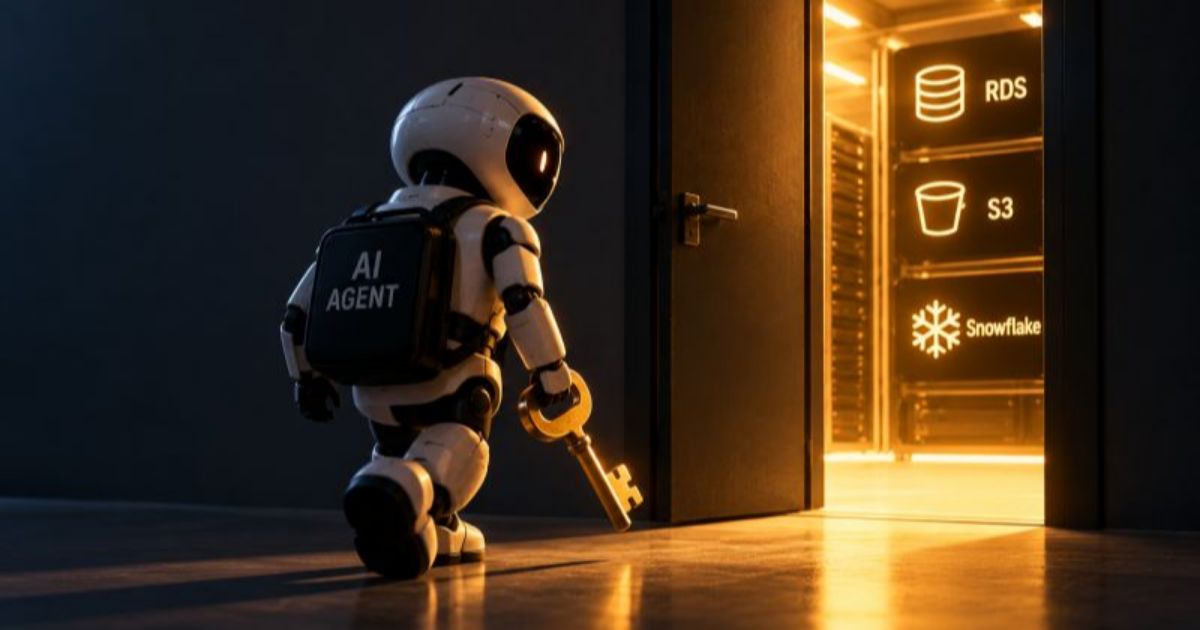
Agents are going live in every organization. Unfortunately, best practices for deployment are lagging behind. A common design pattern is to connect agents to sensitive data sources such as RDS, S3, or Snowflake. I see this especially in two scenarios:
- Custom agents that organizations are building on platforms like AWS AgentCore. These agents act as extensions of the workforce, with access to internal data and systems.
- Developers using Claude Code to connect to and execute queries on databases like RDS, with or without MCP.
In both cases, organizations need to make three fundamental decisions: 1) What identity should the agent have? 2) What credentials should it use? 3) What permissions should it operate under?
I don’t have concrete industry-wide data, but anecdotally, from my interactions, I’d estimate that 90% of agentic deployments follow one of two patterns:
- Static service accounts, with long-lived credentials and overprivileged roles.
- Reusing human identities, with federated authentication but inheriting the user’s permissions.
This is very similar to the early days of the cloud. Organizations make these choices because they are easy, not because they don’t care about security. Existing IAM, IGA, and PAM solutions haven’t made it easy to implement the basics: 1) unique agent identity, 2) federated authentication using short-lived credentials, and 3) short-lived, task-scoped authorization.
The basics haven’t changed. But agents have changed the game. Last week’s events have shown how AI is accelerating vulnerability discovery. Finding and exploiting obscure vulnerabilities used to require significant human effort and ingenuity. AI is rapidly commoditizing this capability.
I predict a similar story with overprivileged identities and static credentials. An agent doesn’t need to be compromised to cause damage. It can misinterpret instructions or make poor decisions while exercising its legitimate permissions, autonomously and at machine speed.
The agent doesn’t have to go rogue. It just has to be wrong.
Unlike the cloud, where organizations spent years accumulating privilege and then trying to clean it up, I expect the shift toward preventative authorization controls to happen much faster with agents. Reactive controls that detect malicious behavior after an agent has already exercised excessive authorization won’t be enough. We need to constrain what agents can do in the first place.
This is exactly why we’re building P0. I’ll share more about best practices for agentic IAM over the coming days.