Resource | Webinar

Your agent reached the MCP gateway. Now what?

MCP has become an important part of the agent security conversation, and for good reason. It gives teams a clean way to connect agents to tools, govern which tools they can call and bring more consistency to how those interactions are managed. 

But the MCP layer sits in the middle of a much longer action chain. A user or another agent starts the task, the agent decides what it needs to do, MCP handles the tool interaction and then that tool acts inside a downstream system using whatever permissions are available there. 

That distinction matters because controlling the tool call is not always the same as controlling the final action. 

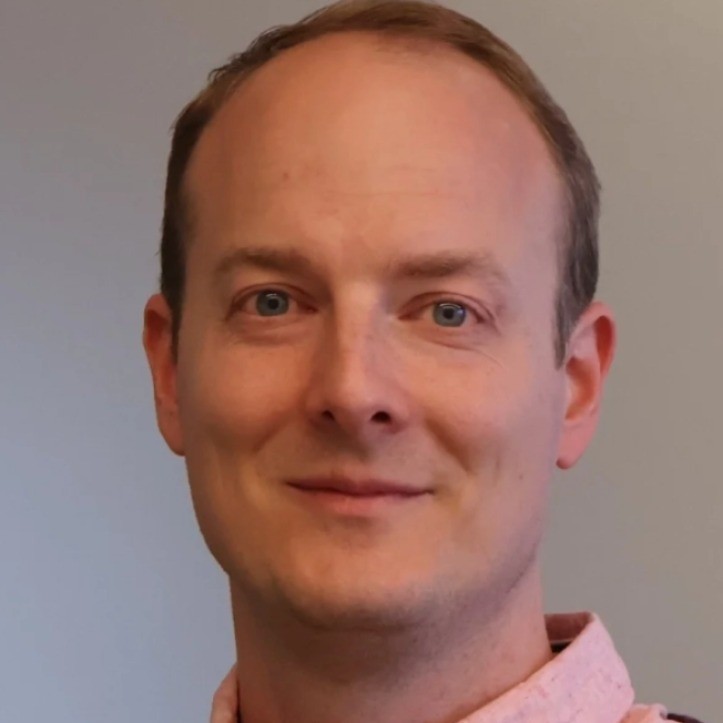
In this 30-minute technical explainer, Neha Duggal and Greg Danyi will map MCP into the full agentic action chain and show where its control point begins and ends. 

They’ll talk about the difference between tool access and target-system authorization, why provenance can get lost as requests move through agents and service accounts and where standing credentials can still leave agents with more access than the task requires. 

This session is for security, identity, platform and AI teams that are already connecting agents to enterprise systems or deciding how they will. 

If you are evaluating MCP gateways, designing your agent security stack or trying to understand whether your current controls cover the full execution path, this will give you a practical way to think about the problem. 
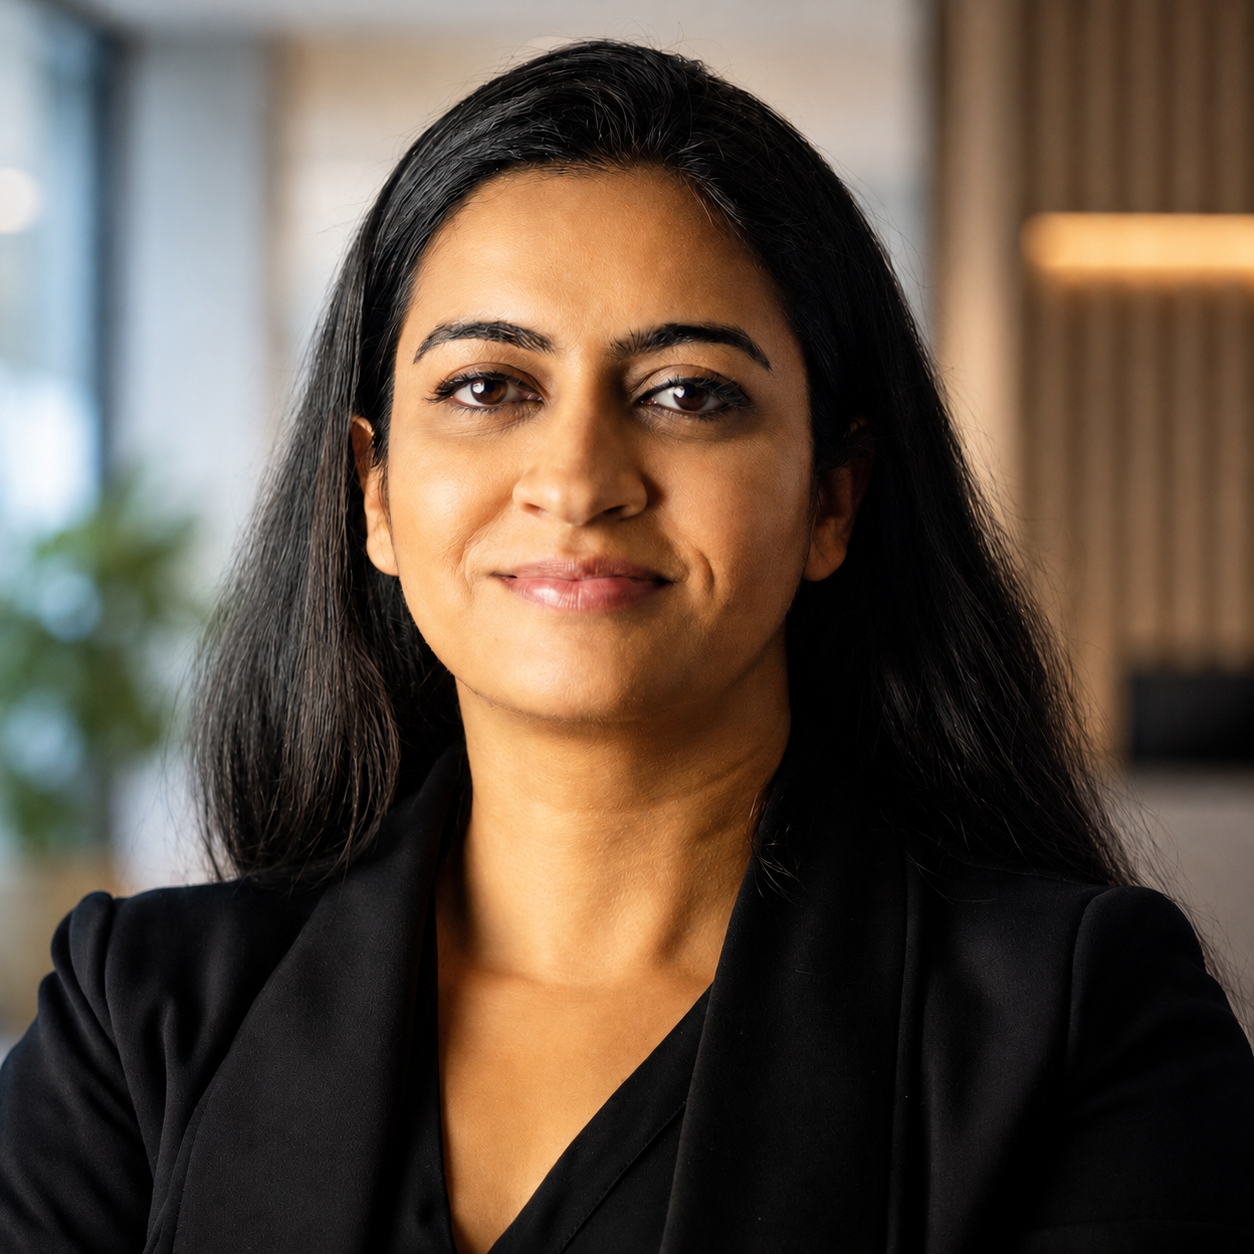
Neha Duggal is an accomplished product leader with deep expertise in cloud security, observability, and enterprise SaaS. With more than 15 years of experience, she has led multiple products from early concept to wide-scale customer adoption, built high-performing cross-functional teams, and driven product strategies that delivered measurable business outcomes. Known for her strong technical grounding and collaborative leadership style, Neha excels at simplifying complex problems, aligning stakeholders, and executing at scale. She has a track record of launching differentiated security capabilities, improving product-market fit, and guiding organizations through periods of rapid growth and transformation. Neha is passionate about building products that deliver real customer value, elevating product excellence within organizations, and mentoring the next generation of product leaders.

Gergely Dányi is the co-founder and Chief Technology Officer at P0 Security, where he leads the development of the first unified identity governance and privileged access management platform purpose-built for the cloud. With deep expertise in cloud security, access management, and startup execution, he’s driving a modern approach that replaces fragmented legacy tools with an identity-native platform that governs and secures all forms of access across hybrid environments. Gergely’s work at P0 centers on eliminating privilege sprawl and enabling just-in-time, policy-driven controls that scale with today’s complex infrastructure, and he’s recognized for pushing the boundaries of how organizations think about secure access in the cloud era.