

At a glance
- GCP temporary access is a role binding with an expiry, set with an IAM condition on request.time.
- IAM conditions cannot be used with basic roles, and the expired binding stays in the policy.
- Google Cloud Privileged Access Manager adds requestable, just-in-time grants that are removed automatically when they end.
- P0 adds Slack and CLI requests, approvals and automatic removal across clouds.
Granting Temporary Access in Google Cloud with Conditional IAM
Do your cloud environments end up cluttered with excess permissions that are no longer being used?
Engineers will often need access to a production cloud environment for brief periods of time: maybe access for an hour to debug a production incident, or access for a week related to a feature they’re working on. If this is addressed by granting them the required access normally, it’s likely they’ll end up with this access for much longer than needed: manually revoking the access once they’re done using it is easy to forget and can quickly become a lot of effort as the number of engineers requesting access increases.
It turns out that Google Cloud natively supports a solution to this problem by allowing you to attach an IAM condition containing an expiration time to a role binding. In this blog post, I’ll walk you through this process. I’ll also cover the other ways to grant GCP temporary access and have it end on its own, including Privileged Access Manager.
Why use temporary access?
- Improve your security posture by removing permanent grants to sensitive resources and granting temporary access when needed.
- Prevent engineers from unintentionally impacting production environments by ensuring they only have production access when they need to use it.
- Simplify access reviews by reducing the number of permanent grants in the system
- Permanent grants to overly privileged roles may violate compliance requirements, while temporary grants are generally fine
Implementation via conditional IAM
You’ll add an IAM condition to the role binding that specifies the expiration. After the expiration, the role binding will still exist, but it will no longer grant any access because the condition will evaluate to false.
Google Cloud conditional IAM attaches a Common Expression Language (CEL) condition to a role binding, which only grants access while the condition is true. GCP IAM condition expiration is just a request.time comparison (see Google’s Configure temporary access guide):
request.time < timestamp(“2020-07-01T00:00:00.000Z”)
To start, you’ll need the appropriate permissions to manage IAM policies on whatever resource you want to add the temporary binding on. For example, if you want to grant temporary access on a project, you’ll need resourcemanager.projectIamAdmin.
Using the Google Cloud Console
Begin by going to the “Grant access” page for your desired resource.
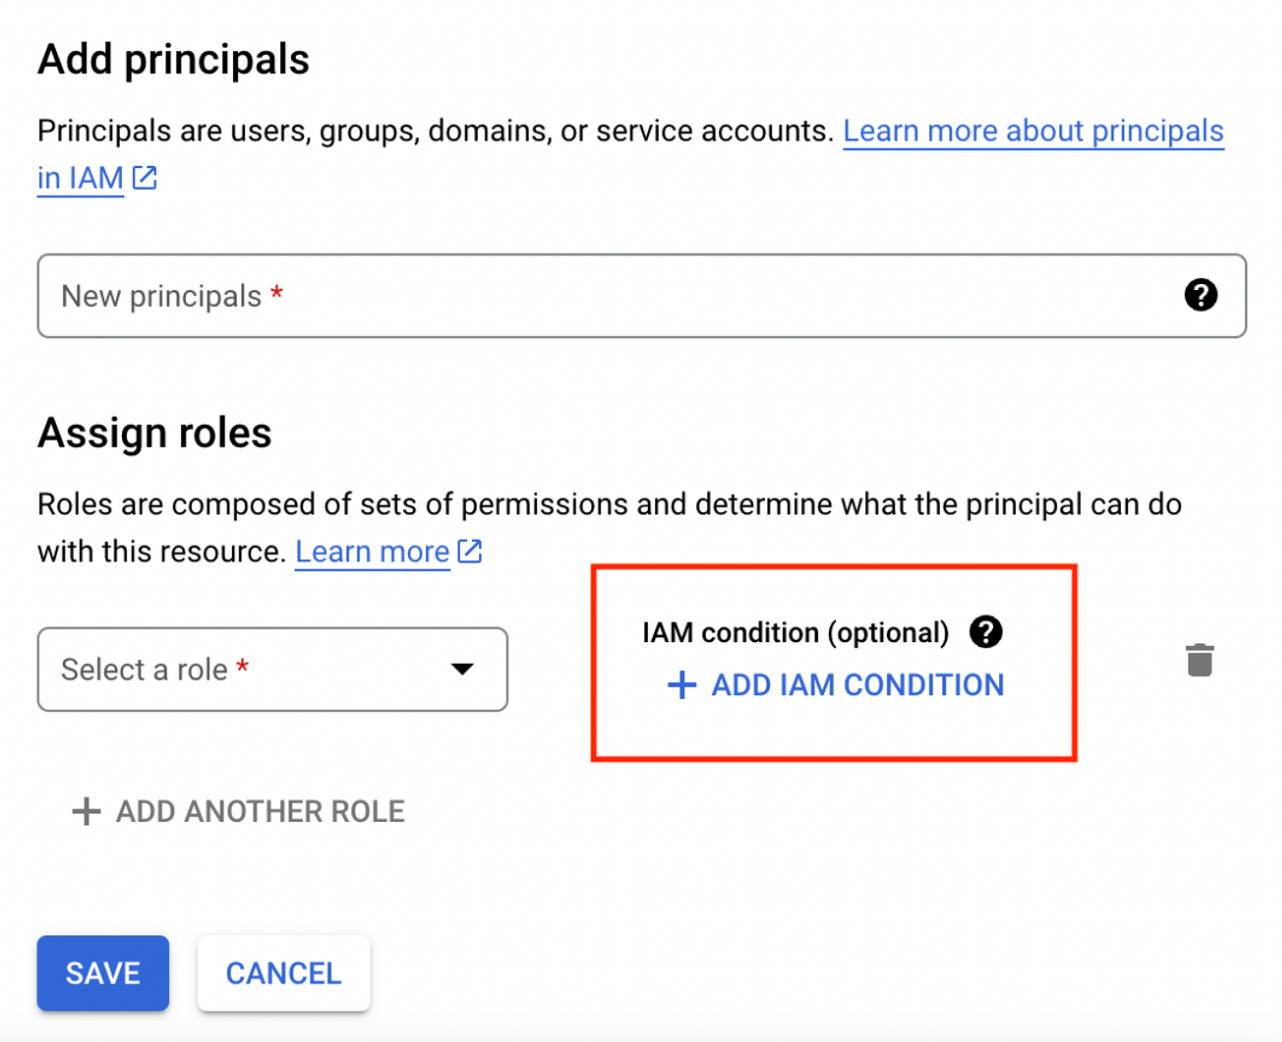
Specify the role and principal, and then click “Add IAM Condition”.
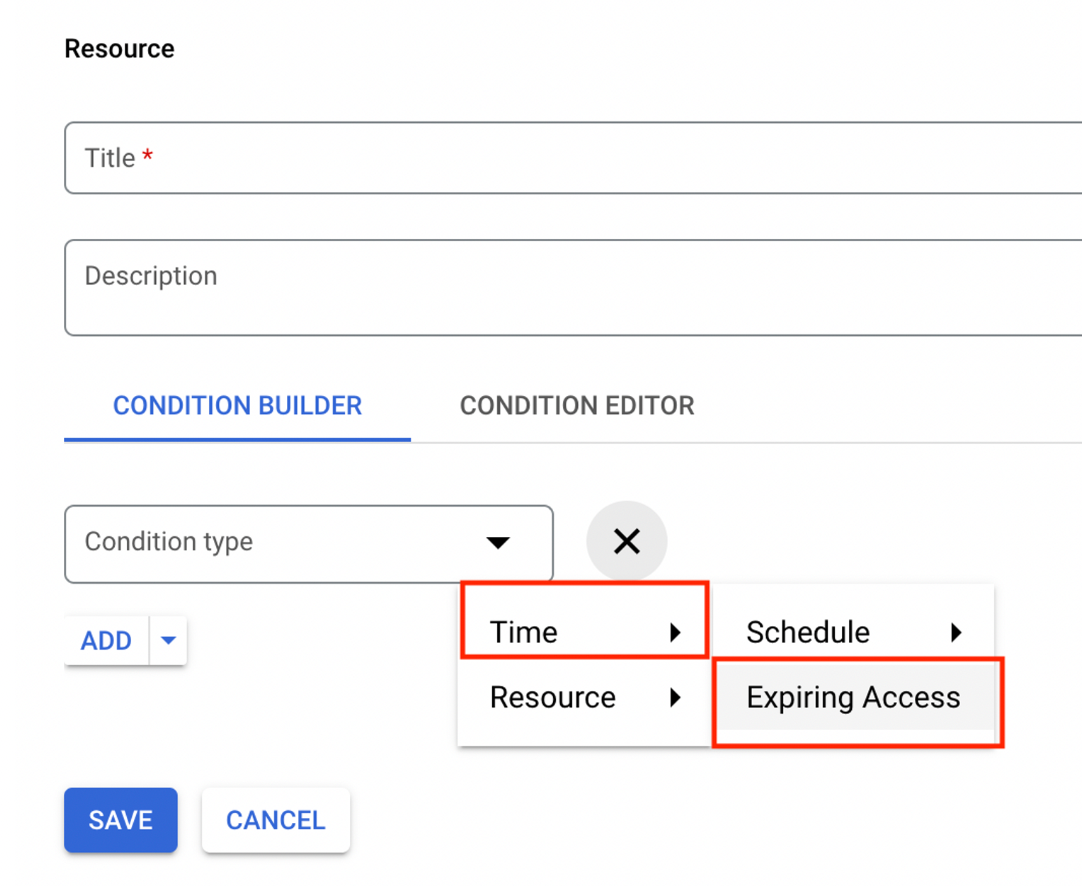
Next, in the condition builder, set “Condition type” to “Expiring Access”.
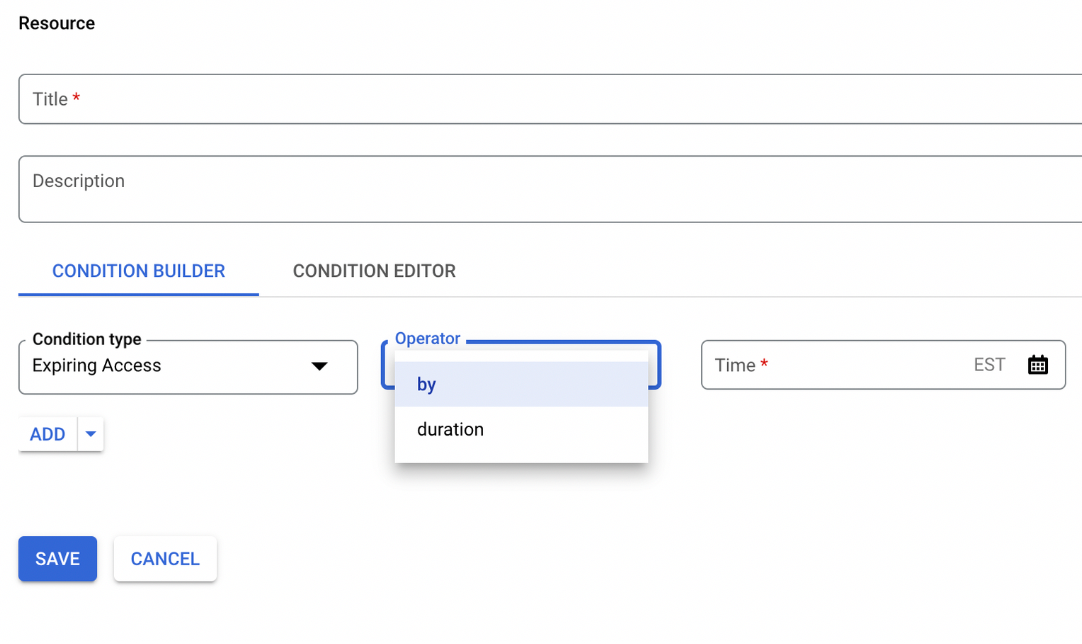
Finally, you can specify your expiration either by entering an expiry timestamp or by specifying a duration.
Add a descriptive condition title and name, click save, and you’re all set.
Directly set policy (CLI or API)
To update an IAM policy via the gcloud CLI or REST API, first get the current IAM policy. For projects, this can be done via gcloud projects get-iam-policy or the Resource Manager API’s projects.getIamPolicy method.
The IAM policy is in the following format, with an array of role bindings.
{
“bindings”: [
{
“members”: [ “user:my-user@example.com” ],
“role”: “roles/owner”
}
],
“etag”: “BwWKmjvelug=”,
“version”: 3
}
You will now add a new binding with your desired member and role with the following IAM condition expression:
request.time < timestamp(‘EXPIRY_TIMESTAMP’)
For example, if you are adding user:test@example.com to iam.securityReviewer with an expiry of July 1, 2027 you would create the following binding:
{
“members”: [ “user:test@example.com” ],
“role”: “roles/iam.securityReviewer”,
“condition”: {
“title”: “Expires_July_1_2027”,
“description”: “Expires on July 1, 2027”,
“expression”: “request.time < timestamp(‘2027-07-01T00:00:00.000Z’)”
}
}
Next, add the new binding to the list of bindings in the existing IAM policy. Note that even if an existing binding exists to iam.securityReviewer , you’ll still want to create this new binding in order to add the condition.
Finally, you can set the IAM policy via the Resource Manager API’s projects.setIamPolicy method, or through gcloud projects set-iam-policy.
For a single binding, Google also documents a one-line form in its Manage access guide:
gcloud RESOURCE_TYPE add-iam-policy-binding RESOURCE_ID \
–member=PRINCIPAL –role=ROLE_NAME \
–condition=CONDITION
Limitations
Although IAM conditions are a great way to implement ephemeral access to your Google Cloud environments, there are a few limitations to this approach.
Basic roles cannot be used with IAM conditions. This means you cannot temporarily grant Viewer, Editor, or Owner using this method. As Google puts it, “You cannot use conditions when you grant legacy basic roles, including Owner (roles/owner), Editor (roles/editor), and Viewer (roles/viewer).”
Only some resource types accept conditions (see Google’s list of supported services), and Cloud Storage buckets also need uniform bucket-level access enabled. In order to grant temporary access to these resources, you would need to grant the role binding on a parent resource that does support conditions (such as the project).
The bindings are not deleted when the access is no longer active. This can make IAM policies harder to understand after some time, since they can get cluttered with expired bindings. Google also advises: “As a best practice, don’t add more than 100 conditional role bindings to a single allow policy.”
GCP just-in-time access options compared
Here is how the main GCP just-in-time access options handle temporary access in Google Cloud:
| Option | How access is granted | Revoked automatically? | Best for |
| IAM Conditions (request.time) | An admin adds a role binding with an expiry | Access stops at expiry; the binding stays in the policy | One-off grants with a known end time |
| Privileged Access Manager | Principals request grants against admin-defined entitlements, with optional approval | Yes, the granted roles are removed when the grant ends | Requestable JIT elevation in Google Cloud (projects, folders, organizations) |
| JIT Groups (open source) | Self-service, group-based access requests | See the JIT Groups docs | Teams willing to deploy and run it themselves |
| P0 Security | Requests from Slack or the P0 CLI, approved per policy | Yes, P0 removes the binding when access expires | Request and approval workflows across clouds |
How to choose: IAM Conditions for one-off grants, Privileged Access Manager for requestable access inside Google Cloud, JIT Groups if you want to self-host, and P0 for request and approval workflows across clouds.
Want to stop manually editing IAM policies? Let P0 automate temporary access
Are you tired of grappling with complex access management processes that slow down your team’s productivity? Say hello to P0 Security, the ultimate solution to streamline access control and elevate your team’s efficiency. You can use our app to grant temporary access to Google Cloud without running a single gcloud command.
After P0 is installed, users can request access simply by typing /p0 request into Slack. Once the request is created, any configured user can approve it by specifying an expiration time and clicking a button on the Slack message. Once a request is approved, P0 automatically provisions the access for the user, and will automatically revoke the access after the expiration time.
Prefer the terminal? The same request works from the P0 CLI, and P0 will revoke GCP access automatically when it expires:
p0 request gcloud role roles/viewer \
–project my-gcp-project \
–reason “Ad-hoc data audit” \
–wait
For Google Cloud, we include the expiration as an IAM condition whenever possible, but we’ll also remove the binding after the access has expired. This allows us to bypass Google Cloud’s limitations and grant any type of access on a temporary basis, even if conditional IAM isn’t supported. Additionally, it ensures that your IAM bindings aren’t cluttered with expired accesses.
Key takeaways
- Use an IAM condition on request.time for one-off temporary access in Google Cloud.
- Conditions don’t work with basic roles, and expired bindings pile up; Google suggests no more than 100 conditional bindings per policy.
- Use Privileged Access Manager for requestable grants that are removed when they end.
- Use P0 for Slack and CLI requests, approvals and cleanup across clouds.
To learn more about how P0 can automate access for your team, view a guided tour of our workflows, head over to our docs for more details, or create an account to get started. You can also join our community Slack channel to engage with like-minded users.
Frequently asked questions
How do you manage and secure gcloud and Google Cloud CLI access for engineers?
Teams manage and secure gcloud and Google Cloud CLI access by replacing standing service account credentials with just-in-time, task-scoped permissions for each engineer.
What are the risks of standing access through gcloud credentials?
Standing access through gcloud credentials risks leaving long-lived, broad permissions active long after an engineer’s task is complete.
How do you grant just-in-time, least-privilege access to Google Cloud resources?
Teams grant just-in-time, least-privilege access to Google Cloud resources by issuing ephemeral credentials scoped to the specific task and automatically revoking them afterward.
How does P0 Security automate short-lived access for Google Cloud workflows?
P0 Security automates short-lived access for Google Cloud workflows by granting time-bound gcloud permissions on request instead of standing credentials.
How does conditional IAM work in Google Cloud?
Conditional IAM in Google Cloud attaches a CEL condition to a role binding, so an expression such as request.time < timestamp(…) grants access only until the expiry; conditions cannot be used with basic roles like Owner, Editor or Viewer.
How do you automatically revoke GCP access after a set time?
An expiring IAM condition stops access at the set time but leaves the binding in the policy, while Privileged Access Manager and P0 remove the grant itself when it ends, so nothing is left to clean up.