
Privilege governance
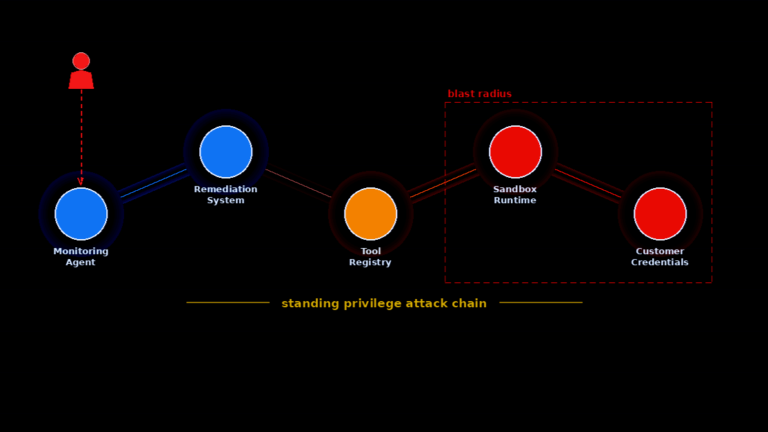
The Composio breach: Let’s stop blaming the agents
By Neha Duggal
The Composio breach was not only about agentic AI, leaked credentials or sandbox execution. It was about trusted internal systems with enough standing privilege to become an attack path.
OAuth scopes don’t equal secure MCP authorization
OAuth scopes solve an important part of the authorization puzzle: delegated capability. But they are only one piece. To do MCP authorization properly, you need scopes for the big picture and server-side RBAC for least-privilege enforcement.