
Shashwat Sehgal
Latest research and insights
P0 raises $5 million in seed funding led by Lightspeed Venture Partners to secure access for cloud-native companies
Announcing P0’s general availability! P0 is the first unified offering...
Non-Human Identities (NHIs) vs. Machine Identities: Key Differences & Security Best Practices
Discover the key differences between Non-Human Identities (NHIs) and machine identities. Learn best practices to secure service accounts, API keys, and cloud assets.
Access granted: the future of identity in the cloud
I'm excited to kick off a series on rethinking cloud identity for the machine-driven er..
Announcing P0’s beta release!
P0 helps cloud security engineers control entitlements for their devel...
Divvy Homes gains stronger visibility and control with a modern cloud-native privileged access solution
Divvy Homes migrates from a cumbersome legacy PAM solution, gaining co...
Enabling Just-In-Time (JIT) Access for AWS S3 Buckets
This blog post explores the concept of granting temporary access to an...
Granting Temporary Access in Google Cloud
Granting temporary access in Google Cloud with conditional IAM improve...
Why Authentication Is Not Enough For Agents
Logging can tell you something happened. But none of that alone determines whether the action should be allowed, given the full chain of authority behind it.
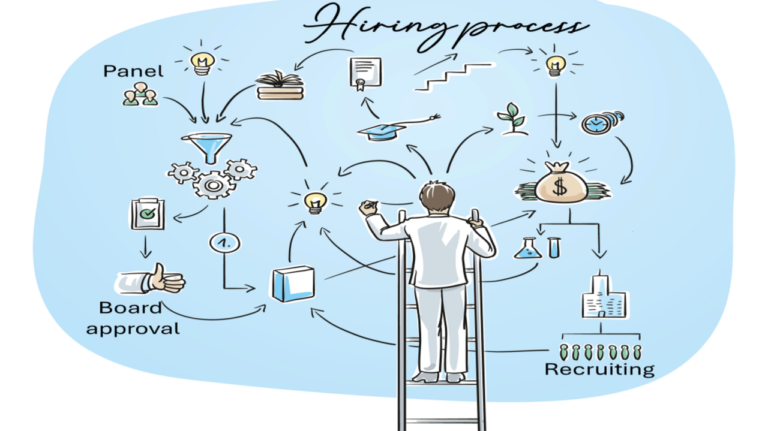
Things I’ve learned about early-stage hiring: stop borrowing big-company process too early
I see a pattern in early-stage companies that is easy to miss because it looks like maturity. Teams borrow processes that work later, when an organization is larger and roles are more specialized, and they apply them far too early.
The day “access” stopped meaning “login” and started meaning “authorization”
Connectivity and authentication have become increasingly commoditized. Most organizations can point to mature tooling, common best practices and a set of controls that are at least defensible.
Every era has its “worked great” tech. Then the environment changes.
If “governing privileged access” still means vaulting static credentials and shared jump-host accounts, you’re solving yesterday’s problem with yesterday’s tools.
When Neha and Kelsey said the quiet part out loud about privileged access
Agentic systems are accelerating everything. They increase the number of access paths, expand the impact of bad permissions and highlight the limits of tools built for manual control.